Cyber Essentials is a UK government-backed certification scheme designed to help organisations protect themselves against common cyber threats. This guide explains the benefits, limitations, and situations where Cyber Essentials is or isn’t worth pursuing, helping business owners, IT managers, and decision-makers make an informed choice.
Quick Summary
- Cyber Essentials is required for many public-sector contracts.
- Cyber Essentials protects against 80% of common cyber threats.
- Achieving Cyber Essentials certification provides a structured path to improve basic security practices and fill gaps before incidents occur.
- Organisations with Cyber Essentials certification may access lower cyber insurance premiums or free coverage.
- Cyber Essentials is considered a low-cost entry point for small and medium-sized enterprises to improve cybersecurity.
- Displaying the Cyber Essentials badge builds customer trust and demonstrates a commitment to data security.
- Certification boosts your reputation and attracts new customers.
- The scheme does not guarantee protection against unauthorised access and advanced, targeted cyber attacks.
It is for business owners, IT managers and anyone weighing Cyber Essentials certification against the fee and the effort, whether a tender has just asked for it or you suspect the Cyber Essentials scheme is a box-ticking exercise.
It is worth it when a customer asks for it, when you have no security baseline, and when you want the free cyber insurance. It is no substitute for real security work. It matters because the wrong answer costs money in both directions: paying for a certificate you cannot use, or losing a contract because you never got one. We see both.
Is Cyber Essentials assessment worth it? The short answer
Worth it when | Not the answer when |
|---|---|
A buyer, tender or supplier questionnaire asks for Cyber Essentials or Cyber Essentials Plus | A buyer wants governance and data protection evidence, or specifically requires ISO 27001 |
You have no security baseline and no clear picture of your IT infrastructure | You would use it in place of penetration testing, backups or an incident response plan |
You are a small organisation with no cyber insurance, and you are eligible for the free cover | You would certify only part of the organisation to get through |
You sell into central government, the NHS or the defence supply chain | The basics are missing, and nobody is asking; fix those first |
Cyber Essentials is the UK government-backed scheme, owned by the National Cyber Security Centre (NCSC) and delivered by IASME, that helps organisations of any size put five basic technical controls in place and prove it to customers. See what is Cyber Essentials? for how the scheme works.
What you are certifying: the Cyber Essentials scope at each level
Cyber Essentials is a UK government-backed scheme that helps protect small businesses against cyber attacks. It includes five key technical controls and is a self-assessment certification. Both Cyber Essentials and Cyber Essentials Plus assess the following five key technical controls:
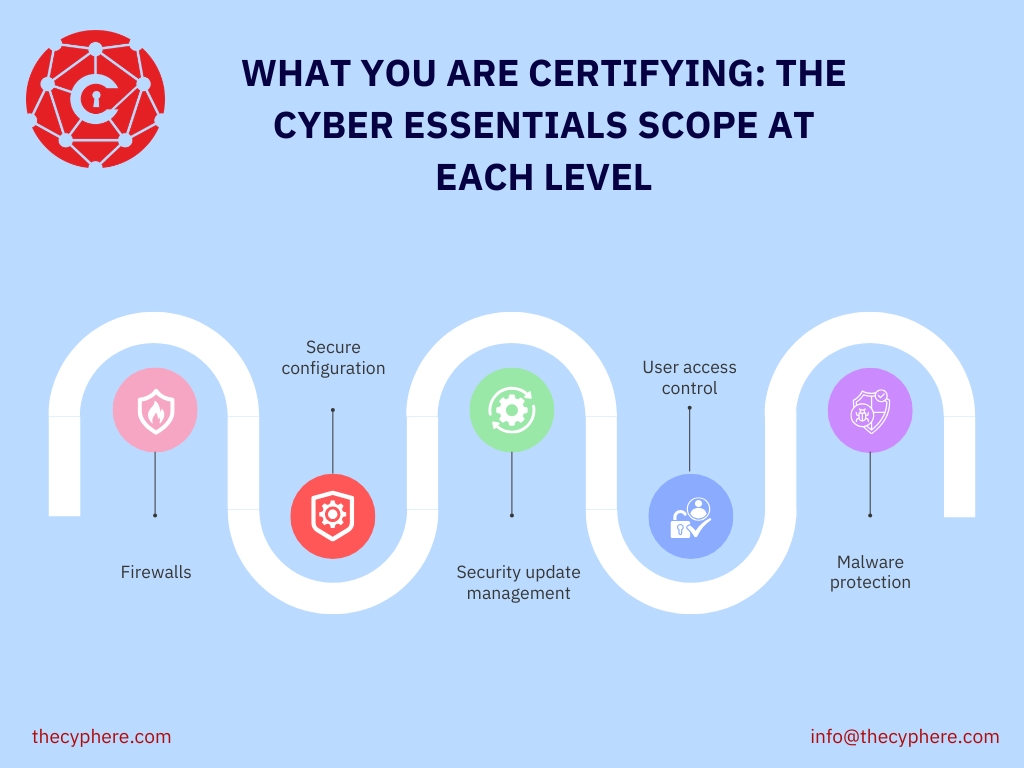
- Firewalls
- Secure configuration
- Security update management
- User access control
- Malware protection
Cyber Essentials is a self-assessment certification, while Cyber Essentials Plus requires an external audit.
Basic Cyber Essentials is a verified self-assessment of these five technical controls. You answer IASME’s self-assessment questionnaire (the Cyber Essentials SAQ), a director or board member signs the declaration, and an assessor at an IASME-licensed certification body marks it, with certification bodies typically reviewing the questionnaire within three days as part of the assessment process.
Cyber Essentials Plus adds an independent technical audit by an accredited certification body of the same controls on a sample of your devices and every cloud service in scope. These audits can take 1-2 weeks. The benefits of Cyber Essentials below apply to both levels; where Plus adds more, we say so. For each control, see Cyber Essentials requirements; for the fees and the costs outside the fee, see our Cyber Essentials cost guide.
Suggested read: Cyber Essentials Plus checklist
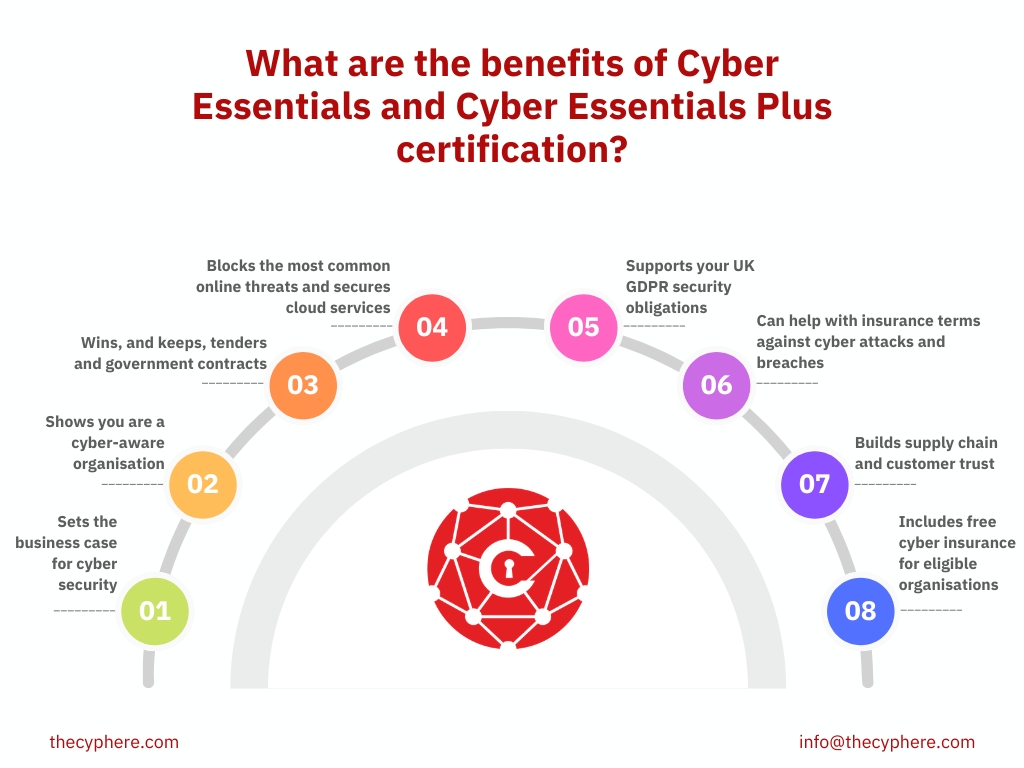
What are the benefits of Cyber Essentials and Cyber Essentials Plus certification?
The benefits of Cyber Essentials fall into three groups: winning and keeping work, reducing the most common risks, and building trust with customers and insurers.
Sets the business case for cyber security
During our CREST penetration testing (and other security services) scoping calls, we often ask questions such as “When was the last time you had an internal penetration test done?”, “How do you manage firewall security, endpoint security and the handling of sensitive data?” and “What password controls and security policies are in place?”
In our experience, many organisations cannot answer those questions with confidence until they have worked through the Cyber Essentials question set as part of the assessment process. Doing so gives them documented answers and a baseline to build a security budget around. With Cyber Essentials Plus certification, an independent assessor has also checked that baseline rather than taking it on trust.
Because a director or board member signs the declaration, the board takes ownership of cyber risk rather than leaving it with IT. The assessor reviews your answers, but the organisation has to check that each of the five controls is really in place before it answers.
This is an intangible yet tangible benefit of Cyber Essentials because it separates your operational IT service delivery from cyber and risk topics. This often opens up senior stakeholders to better accountability and governance for legal, risk and compliance functions to include cyber as a mandatory function.
Suggested read: small business cyber security statistics
Shows you are a cyber-aware organisation
Achieving Cyber Essentials certification starts with listing every device, cloud service and user account in scope, often for the first time, and that is the part of the Cyber Essentials process most organisations get the most from. In our assessments, that scope list regularly identifies user devices and wider IT systems, and it often turns up devices running unsupported software, unsupported operating systems, cloud services without MFA, and high or critical updates left unapplied for more than 14 days.
Under v3.3 (Danzell), those three areas fail an assessment automatically, so finding them before an attacker does is a benefit in itself. See the Danzell changes.
Wins, and keeps, tenders and government contracts
This is the benefit that pays for the certificate most directly. Several buyers make Cyber Essentials a formal condition, and the level they ask for varies:
Buyer | What is required | Where it comes from |
|---|---|---|
Central government | Cyber Essentials for government contracts that involve handling personal data or supplying certain ICT services | Procurement Policy Note 014 (PPN 014 on gov.uk) |
NHS Supply Chain | Cyber Essentials Plus certification for in-scope suppliers complying with DTAC, DSPT | |
Ministry of Defence | Defence Cyber Certification Level 0, which is built on Cyber Essentials, by 31 December 2026 | See DCC Level 0 |
Further education | Colleges are expected to hold Cyber Essentials and renew it every year | College Financial Handbook |
Private-sector buyers increasingly ask for it in supplier questionnaires too, as part of their supply chain security checks, and the certificate can also support wider compliance checks in those forms. Holding the certificate before a tender appears is far easier than certifying inside one. See is Cyber Essentials mandatory? for each requirement and its source.
Blocks the most common online threats and secures cloud services
Firewalls, secure configuration, security update management, user access control and malware protection are the five technical controls under the Cyber Essentials scope. These security controls defend against the common cyber attacks that cyber criminals run at scale: opportunistic, internet-based attempts that succeed because of a missing update, default passwords, an exposed service or an account without MFA. The Cyber Essentials controls are designed around exactly these most common cyber attacks.
There is evidence that it works. IASME reports that insurance data shows certified organisations are 92% less likely to make a claim on their cyber insurance (IASME, December 2025). This makes Cyber Essentials Plus certification a solid foundation marking the beginning of the cyber security maturity journey for an organisation.
Cyber Essentials Plus checks that these controls actually work: an external vulnerability scan of your internet-facing systems, an internal vulnerability scan of sampled devices for missing updates, tests that verify anti-malware software can detect web-delivered and email-borne threats, and checks on MFA on all cloud services (key changes in Danzell) and the separation of admin accounts. Malware protection tools also need daily updates to remain effective.
Supports your UK GDPR security obligations
UK GDPR requires organisations to protect personal data with appropriate technical and organisational measures. Cyber Essentials does not make you GDPR compliant, and it is not a GDPR requirement, though it can support compliance evidence for GDPR without making an organisation compliant by itself. It does give you evidence that a recognised set of technical security measures is in place, which is part of what “appropriate” means for most organisations handling personal data.
Can help with insurance terms against cyber attacks and breaches
A Cyber Essentials Plus certificate gives an insurer independent evidence that the basic controls have been tested on your devices, not just declared. Some insurers and brokers price cyber cover on it, and many ask about it on the proposal form. Some organisations may also see better cyber insurance premiums because insurers treat certification as evidence of good cyber hygiene. It is not a guaranteed discount, so ask your broker directly how they treat it.
Builds supply chain and customer trust
Buyers increasingly check the public IASME register during onboarding and annual supplier reviews, and certified organisations are also listed on the NCSC supplier database. A current certificate answers a set of security questions before they are asked, shortens questionnaires, and shows that someone in your organisation owns security. They can check public certification status in a minute on the iasme website (see our certificate check guide).
Includes free cyber insurance for eligible organisations
Eligible UK organisations that certify their whole organisation receive cyber liability insurance with the basic certificate at no extra cost: a £25,000 limit and a 24-hour incident response helpline. To qualify, you must be domiciled in the UK or Crown Dependencies, have annual turnover under £20 million, and opt in when you certify (IASME’s insurance page).
For a small organisation with no other cover, that is a genuine benefit. Read the terms rather than assuming: the cover has limits and conditions, and a certificate covering only part of the organisation is not eligible.
What Cyber Essentials does NOT cover
Cyber Essentials is a baseline. It does not test your web applications for flaws, detect a targeted attacker who is already inside, address insider misuse, assess whether your people would recognise a well-crafted phishing attempt, or cover every kind of potential threat. It says nothing about backups, incident response or business continuity, which sit outside the five controls and are not assessed.
That is not a weakness of the scheme; it is its design. The controls are aimed at the common cyber threats that arrive unprompted from the internet, reducing exposure to common online risks rather than every type of threat. Where you need to know how far an attacker could get, that is what penetration testing is for.
From the assessor’s desk
Passing Cyber Essentials certification means the basics are in place on the day you were assessed. It does not mean you are secure. A technical finding isn’t a business risk until it’s triaged, prioritised and set against the organisation’s risk appetite, and Cyber Essentials certification is the foundation for that conversation, not the end of it.
Harman Singh, IASME-licensed Cyber Essentials assessor, Cyphere
When is Cyber Essentials not enough?
When a buyer wants evidence of governance, risk management and data protection as well as technical controls, or when they require an international standard. A supplier questionnaire that asks about policies, risk assessments, supplier management and incident response is asking for more than the five controls can show.
For UK organisations in that position, IASME Cyber Assurance builds on the Cyber Essentials certificate and scales to your size; Cyphere is a licensed certification body for Level 1 and Level 2. It is a recognised alternative to ISO 27001, not an equivalent, so check what the customer will accept before you choose. Our framework comparison sets out the options.
How Cyphere helps you decide
From the assessor’s desk
If a buyer is asking for Cyber Essentials certification, it is almost always worth it, and we will tell you which level they need. That helps organisations keep the process more cost-effective by choosing the right certification level, and by understanding how different certification levels fit their needs, since Cyber Essentials Plus costs vary by organisation size and complexity. If nobody is asking, it is still a sensible baseline for most small organisations, and the free insurance and the helpline are real business benefits.
Where it is not enough, because a customer wants governance evidence or an international standard, we will say so and point you to IASME Cyber Assurance or ISO 27001 rather than sell you something that does not answer the question. No fluff, just how it is.
Harman Singh, IASME-licensed Cyber Essentials assessor, Cyphere
Before you start, a readiness tool or tailored prep resource can help you see what needs attention first. Cyphere’s cyber advisors can provide practical support to prepare for certification.
Talk to an IASME-licensed assessor
FAQs
Why is achieving Cyber Essentials certification important?
Because it addresses the attacks most organisations actually face, and because a growing number of buyers require it. For many suppliers, the certificate is the difference between being eligible to bid and not.
Does Cyber Essentials certification guarantee we will not be hacked?
No. It confirms the baseline controls were in place when you were assessed. It significantly reduces exposure to common internet-based attacks, but it does not address targeted attacks, insider misuse or application flaws.
Is Cyber Essentials Plus worth it?
When a buyer asks for it, when you sell into healthcare, defence or the public sector, or when you want independent evidence that the controls work on your systems. Cyber Essentials Plus also includes a technical audit of external-facing systems such as internet gateways, along with checks on sampled user devices and other in-scope IT systems. See Cyber Essentials vs Cyber Essentials Plus.
Who qualifies for the free cyber insurance?
Organisations domiciled in the UK or Crown Dependencies with annual turnover under £20 million that certify their whole organisation and opt in. The cover has a £25,000 limit and a 24-hour incident response helpline. A certificate covering only part of the organisation is not eligible.