Most of the small business cyber statistics that circulate online are American, several years old, and in at least one well-known case made up. The UK has better data than that. The government’s Cyber Security Breaches Survey interviews more than 2,000 businesses every year and publishes almost every result split by size, so we can say with some confidence how micro businesses (1 to 9 staff) and small businesses (10 to 49 staff) are doing compared with medium (50 to 249) and large (250 and over) ones.
In this article we have pulled together the latest statistics on cyber attacks against small businesses from the sources that hold the data: the Cyber Security Breaches Survey 2025/26, City of London Police, DSIT’s research on SME cyber insurance and the economic cost of attacks, the NCSC, IASME, Hiscox’s survey of firms with fewer than 250 staff, the insurers’ claims reports and the Verizon DBIR. UK figures come first in every section. Where a figure is global, European or US-only we say so in the line.
The page is organised around the questions people ask us most: how many small businesses get attacked, what the attacks are, what they cost, how small firms’ defences compare with larger ones, who has insurance, and what to do about it on a small budget.
Key small business cyber attack statistics for 2026 at a glance
- 42% of UK micro businesses and 46% of small businesses identified a cyber breach or attack in the last 12 months, against 65% of medium and 69% of large businesses (Cyber Security Breaches Survey 2025/26, DSIT, April 2026).
- 17% of micro and 24% of small UK businesses were victims of a cyber crime in the last year, compared with 41% of medium and 48% of large businesses (CSBS 2025/26).
- Phishing hit 37% of micro and 40% of small businesses, and 70% of micro businesses that were breached named phishing as their most disruptive incident (CSBS 2025/26).
- The median cost of the most disruptive breach for UK micro and small businesses was £0; the top 5% of cases cost £4,000 or more, rising to £14,440 where the breach had a material outcome (CSBS 2025/26).
- 38% of UK organisations with fewer than 250 staff reported at least one successful cyber attack in the past year, the highest of the eleven countries surveyed, against a 29% average (Hiscox Cyber Readiness Report 2026, fieldwork June 2026).
- 175 of the 323 ransomware attacks reported to UK police between April 2025 and March 2026 came from SMEs (City of London Police, June 2026).
- Only 32% of micro and 39% of small businesses have a policy to apply security updates within 14 days, against 73% of large businesses; 43% of micro and 58% of small businesses require two-factor authentication, against 90% of large (CSBS 2025/26).
- 8% of micro and 15% of small businesses hold a specific cyber insurance policy; 33% of micro businesses say they have no cyber cover at all (CSBS 2025/26).
- 14% of micro and 25% of small businesses have heard of Cyber Essentials; 12% of small businesses now hold it, up from 5% a year earlier (CSBS 2025/26).
- Across Chubb’s EMEA book, the average SME cyber claim reached $82,621 in 2025, a five-year high, and SME claim frequency rose 86% in a year (Chubb EMEA Cyber Claims Report 2026).
1. How many UK small businesses are attacked?
There are 5.69 million private sector businesses in the UK and 99.9% of them are SMEs. Three quarters have no employees at all. Of the rest, 1.15 million are micro businesses with 1 to 9 staff, 220,000 are small businesses with 10 to 49, 38,000 are medium and 8,300 are large (Business Population Estimates 2025, Department for Business and Trade, October 2025). The Cyber Security Breaches Survey covers businesses with at least one employee, so when it reports a percentage of micro businesses, the base is roughly 1.15 million firms.
- 43% of all UK businesses identified a cyber security breach or attack in the 12 months before the survey, which DSIT extrapolates to about 612,000 businesses (CSBS 2025/26, fieldwork autumn 2025, published 30 April 2026).
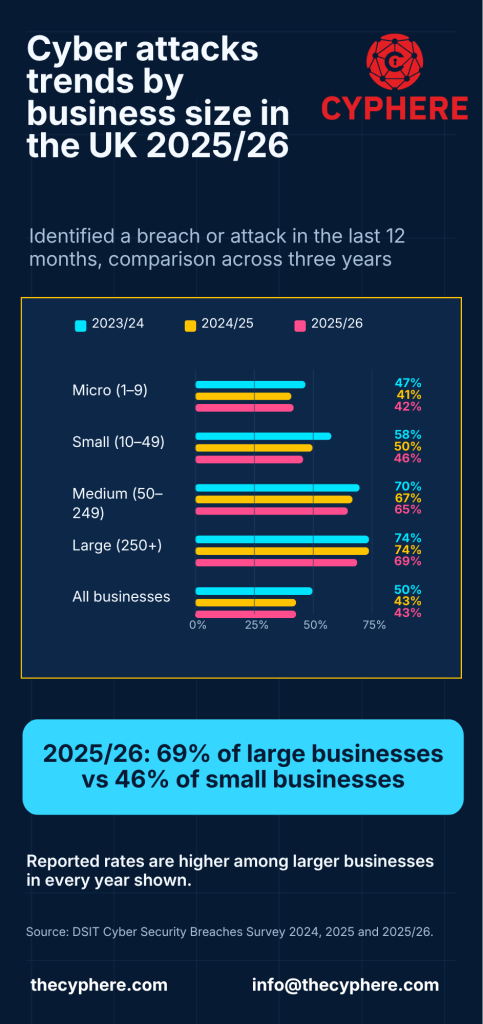
- By size: 42% of micro businesses, 46% of small, 65% of medium and 69% of large businesses identified a breach or attack (CSBS 2025/26).
- 19% of businesses were victims of at least one cyber crime under the Computer Misuse Act definition, about 267,000 businesses. By size: 17% of micro, 24% of small, 41% of medium and 48% of large (CSBS 2025/26).
- Among micro and small businesses that identified any breach, the pattern is repeat exposure rather than a single event: across all businesses, 27% of those breached said it happened roughly once a month, 16% once a week and 13% daily or more (CSBS 2025/26).
- DSIT estimates UK businesses experienced about 5.19 million cyber crimes of all types in the year, including roughly 70,000 that were not phishing (CSBS 2025/26).
- 38% of UK organisations with fewer than 250 employees reported at least one successful cyber attack in the previous 12 months, the highest rate of any country in the study, against a global average of 29% and 20% in the United States; affected firms reported an average of four successful attacks (Hiscox Cyber Readiness Report 2026, 6,800 respondents including 1,000 in the UK, fieldwork 5 to 17 June 2026).
The two sources measure different things. CSBS counts any identified breach or attack, including phishing emails that were never opened, and its micro and small figures are lower than medium and large partly because smaller firms have less monitoring and notice less. DSIT says so in the report. Hiscox counts successful attacks as reported by the people running cyber security in firms under 250 staff, which is why its UK number is close to the CSBS figure for all businesses.
Trend by business size
| Identified a breach or attack in the last 12 months | 2023/24 | 2024/25 | 2025/26 |
|---|---|---|---|
| Micro (1 to 9 staff) | 47% | 41% | 42% |
| Small (10 to 49) | 58% | 50% | 46% |
| Medium (50 to 249) | 70% | 67% | 65% |
| Large (250+) | 74% | 74% | 69% |
| All businesses | 50% | 43% | 43% |
Source: DSIT Cyber Security Breaches Survey 2024, 2025 and 2025/26. The fall between 2023/24 and 2024/25 was driven by fewer micro and small businesses identifying phishing. DSIT changed the question wording in 2023/24, so earlier years are not comparable.
Suggested Read: Cyber Security Statistics
2. The most common cyber attacks on small businesses
Phishing dominates at every size, but the gap between small and large businesses opens up on everything else. Larger firms report more impersonation, malware and ransomware, partly because there is more of it and partly because they have the tooling to see it.
| Type of breach or attack identified in the last 12 months | Micro | Small | Medium | Large | All |
|---|---|---|---|---|---|
| Phishing | 37% | 40% | 60% | 63% | 38% |
| Impersonation of the organisation or staff in emails or online | 10% | 17% | 38% | 47% | 12% |
| Devices targeted with malware (viruses, spyware) | 7% | 7% | 12% | 23% | 7% |
| Hacking or attempted hacking of online bank accounts | 4% | 2% | 3% | 5% | 3% |
| Denial of service | 3% | 2% | 5% | 9% | 3% |
| Takeovers of website, social media or email accounts | 2% | 3% | 5% | 5% | 2% |
| Ransomware | 1% | 2% | 3% | 7% | 1% |
| Any breach excluding phishing | 20% | 22% | 47% | 55% | 21% |
Source: CSBS 2025/26 data tables, Table 28. Bases: 1,154 micro, 507 small, 296 medium, 155 large businesses.
- Phishing among small businesses has fallen from 49% in 2023/24 to 40% in 2025/26, and ransomware among micro businesses from 3% to 1% over the same period (CSBS 2025/26).
- 70% of micro businesses that experienced a breach named phishing as the most disruptive one, against 59% of medium and 53% of large businesses, who were more likely to point to impersonation (CSBS 2025/26).
- Among breached businesses, the reasons phishing was disruptive were staff time investigating potential attacks (21%), time needed for staff training (12%) and downtime while investigations ran (12%) (CSBS 2025/26).
- Phishing accounted for 93% of the cyber crimes businesses experienced; 3% of all businesses experienced a non-phishing cyber crime such as hacking, ransomware or malware that got past their defences (CSBS 2025/26).
- 3% of businesses, roughly 43,000 firms, experienced fraud as a result of a cyber breach, with an estimated 130,000 cyber-facilitated fraud events across the business population (CSBS 2025/26).
Ransomware and small firms
- 323 UK organisations reported a ransomware attack to Report Fraud between April 2025 and March 2026, and 175 of them, more than half, were SMEs. Where the sector was recorded, manufacturing (42 reports), scientific and technical (21) and education (19) were the most affected. Police say the figures are heavily under-reported (City of London Police, 29 June 2026).
- Globally, about 96% of ransomware victims in the Verizon dataset where organisation size was known were SMBs, which Verizon defines as under 1,000 employees. The attacks were opportunistic: victims had compromised credentials (38%) or unpatched vulnerabilities in edge devices (29%) rather than being chosen for their industry or revenue (Verizon DBIR 2026, global, 7,152 SMB breaches analysed).
- Small organisations in the Verizon dataset experienced a median of seven credential-leak events over the year, against around 20 for larger organisations (DBIR 2026, global).
- Across all organisations, ransomware featured in 48% of breaches analysed, 69% of victims did not pay, and the median ransom paid fell to $139,875 (DBIR 2026, global).
The Verizon definition of small, under 1,000 staff, would cover every UK business except the 8,300 large ones, so treat the 96% as a statement about who ransomware groups hit rather than a UK small-firm rate. The UK rate is in the table above: 1% of micro and 2% of small businesses in the last year.
Suggested Read: Phishing Statistics
3. What a cyber attack costs a small business
The honest answer from the UK data is that most identified breaches cost nothing, and a small minority cost a great deal. DSIT stopped publishing mean costs in 2025/26 because a handful of large incidents distorted them, and now reports medians and percentiles instead. The figures below are for the single most disruptive breach in the last 12 months.
| Perceived cost of the most disruptive breach | Micro and small | Medium and large | All businesses |
|---|---|---|---|
| Median, all businesses identifying a breach | £0 | £30 | £0 |
| Top 10% of cases (90th percentile) | £1,140 | £2,330 | £1,500 |
| Top 5% of cases (95th percentile) | £4,000 | £10,000 | £4,000 |
| Median, excluding £0 answers | £200 | £300 | £200 |
| 95th percentile, excluding £0 answers | £8,300 | £28,200 | £10,000 |
| Median, breaches with a material outcome | £560 | £570 | £560 |
| 95th percentile, breaches with a material outcome | £14,440 | base too small | £15,000 |
Source: CSBS 2025/26, Tables 4.1a, 4.1b and 4.2a. Micro and small are combined by DSIT for sample size (base 680).
- 19% of businesses that identified a breach suffered a negative outcome from it; among micro businesses it was 18% and among small businesses 20%. The most common outcomes were temporary loss of access to files or networks (8%) and websites or online services taken down or slowed (6%) (CSBS 2025/26).
- 5% of businesses that were breached reported a loss of revenue or share value, up from 2% the year before, and 3% reported reputational damage, up from 1% (CSBS 2025/26).
- 86% of micro businesses were back to normal within a day after their most disruptive breach, down from 92% in each of the two previous years; 10% of micro businesses took between a day and a week (CSBS 2025/26).
- The median cost of a non-phishing cyber crime was £250 including those who said £0, and £750 excluding them; the top 10% of cases cost £5,000 to £7,500 (CSBS 2025/26).
- Among businesses hit by cyber-facilitated fraud, the median loss was £500 excluding £0 answers and the top 10% of cases cost £12,000 to £15,000 (CSBS 2025/26).
- 32% of firms under 250 staff that were attacked reported delays to growth or new initiatives, 31% higher staffing or external expertise costs, 30% a negative effect on financial performance, valuation or credit rating, and 29% lost business opportunities or partnerships (Hiscox 2026, eleven countries).
- Cyber incidents cost firms under 250 staff about $52,602 a year on average and 32.8 hours of operational downtime per hack across the study (Hiscox 2026, global average). UK press coverage of the report put the UK average cost per attack at £26,650.
- Independent research for DSIT estimates that cyber attacks cost the UK economy about £14.7 billion a year, 0.5% of GDP, with an average cost per significant attack of almost £195,000 across all sizes and sectors. The modelling is built largely on US incident data and DSIT describes it as indicative (KPMG for DSIT, Economic impact of cyber attacks, November 2025).
- In FSB’s last survey of its members, covering January 2021 to January 2023, the most impactful cyber crime or fraud cost 43% of affected small firms £1,000 or less, 21% between £1,001 and £25,000, 3% between £25,001 and £100,000 and 2.5% more than £100,000 (FSB, Cracking the Case, 2023 data; the newest FSB figures available).
- Across Chubb’s EMEA policyholders, the average SME claim (revenue up to $99 million) reached $82,621 in 2025, a five-year high, while SME claim frequency rose 86% between 2024 and 2025; mid-market claims averaged $318,820 (Chubb EMEA Cyber Claims Report 2026, Europe, Middle East and Africa).
- Coalition’s policyholders with revenue over £100 million had a claims frequency five times higher than smaller organisations in 2025, and the highest average loss at about £201,700; the average across all claims was about £87,000 (Coalition 2026 Cyber Claims Report, UK, US, Canada, Australia and Germany).
Our view is that the two sets of numbers are both right. The survey median of £0 describes the hundreds of thousands of phishing emails that get deleted. The insurer averages describe what happens on the day one of them does not get deleted, and a five-figure or six-figure bill lands on a firm with a small-business balance sheet.
Suggested Read: Cyber Insurance Statistics
4. Small business cyber security: the gap between small and large firms
This is the centrepiece of the UK data and the part nobody else publishes as a table. Every row is from the CSBS 2025/26 data tables, all UK businesses, bases of 1,154 micro, 507 small, 296 medium and 155 large unless noted.
| Control, process or arrangement in place | Micro | Small | Medium | Large | All |
|---|---|---|---|---|---|
| Up-to-date malware protection | 80% | 85% | 91% | 93% | 81% |
| Firewalls covering the whole network and devices | 72% | 82% | 89% | 93% | 74% |
| Backing up data securely via a cloud service | 73% | 80% | 84% | 79% | 74% |
| Restricting admin and access rights to specific users | 69% | 86% | 96% | 96% | 73% |
| Password policy requiring strong passwords | 72% | 79% | 94% | 96% | 74% |
| Security controls on company-owned devices | 57% | 79% | 90% | 91% | 61% |
| Agreed process for staff who spot a fraudulent email | 54% | 72% | 86% | 94% | 58% |
| Two-factor authentication for networks or applications | 43% | 58% | 79% | 90% | 47% |
| VPN for staff connecting remotely | 32% | 48% | 72% | 72% | 36% |
| Policy to apply security updates within 14 days | 32% | 39% | 56% | 73% | 34% |
| Monitoring of user activity | 29% | 46% | 68% | 82% | 33% |
| Cyber security risk assessment in the last 12 months | 26% | 41% | 62% | 72% | 30% |
| Cyber security vulnerability audit | 15% | 28% | 46% | 59% | 18% |
| Penetration testing | 10% | 21% | 38% | 60% | 13% |
| Staff training or awareness sessions | 14% | 33% | 54% | 84% | 19% |
| Formal policy covering cyber security risks | 31% | 52% | 75% | 89% | 36% |
| Business continuity plan covering cyber security | 29% | 44% | 73% | 85% | 33% |
| Formal incident response plan | 21% | 36% | 57% | 76% | 25% |
| None of the listed incident response measures | 48% | 33% | 16% | suppressed | 45% |
| Board member or senior manager responsible for cyber security | 29% | 37% | 52% | 68% | 31% |
| Cyber security a high priority for senior management (half sample) | 69% | 82% | 92% | 100% | 72% |
| Formally reviewed risks from immediate suppliers | 12% | 22% | 30% | 48% | 15% |
| External cyber security provider | 44% | 64% | 70% | 42% | 48% |
| Sought external information or guidance (half sample) | 41% | 58% | 71% | 61% | 44% |
| Aware of Cyber Essentials (half sample) | 14% | 25% | 56% | 64% | 17% |
| Rule or policy not to pay ransomware demands (half sample) | 50% | 50% | 40% | 39% | 49% |
Source: CSBS 2025/26 data tables, Tables 1, 7, 9, 12, 15, 17, 19, 26 and 41.
Some points from the detail:
- Micro businesses improved on two controls in a year: restricting access to company-owned devices rose from 58% to 64%, and two-factor authentication from 35% to 43% (CSBS 2025/26).
- Small businesses went the other way. Risk assessments fell from 48% to 41%, formal cyber security policies from 59% to 52% and business continuity plans covering cyber from 53% to 44%, back to their 2023/24 levels (CSBS 2025/26).
- 30% of micro businesses say cyber security is a low priority for their senior management, against 8% of medium and none of the large businesses sampled (CSBS 2025/26).
- Only 3% of micro businesses have someone in an IT role looking after cyber security; it is usually the owner, the chief executive or another senior manager. In small businesses the most common person responsible is the general office manager (26%) (CSBS 2025/26).
- 24% of all businesses report having technical controls in all five Cyber Essentials areas, rising to 51% of medium and 70% of large businesses (CSBS 2025/26).
- 13% of micro and 17% of small businesses have heard of the NCSC’s Small Business Guides, and 10% of micro and 13% of small businesses have heard of the Cyber Action Plan for small organisations (CSBS 2025/26).
- 36% of micro businesses that undertook a vulnerability audit used external contractors only, as did 47% of small businesses (CSBS 2025/26).
- After their most disruptive breach, 58% of micro businesses and 69% of small businesses took some action to prevent a repeat, against 84% of large businesses; 39% of micro businesses did nothing (CSBS 2025/26).
- 39% of micro and 42% of small businesses reported their most disruptive breach to anyone outside the organisation (CSBS 2025/26).
The rows that matter most are patching within 14 days, two-factor authentication and the incident response line. A micro business is twice as likely as a large one to be missing MFA and patching, and nearly half of micro businesses have no incident response arrangements at all. Those are exactly the gaps that the opportunistic ransomware operators in the Verizon data are scanning for.
Suggested Read: Penetration Testing Statistics
5. Cyber insurance and small businesses
| Insurance position (half sample) | Micro | Small | Medium | Large | All |
|---|---|---|---|---|---|
| Specific cyber insurance policy | 8% | 15% | 24% | 32% | 10% |
| Cyber cover as part of a wider policy | 37% | 40% | 36% | 22% | 37% |
| Any cyber cover | 45% | 55% | 61% | 54% | 47% |
| Not insured against cyber risks | 33% | 20% | 10% | 9% | 31% |
| Do not know | 22% | 25% | 30% | 37% | 22% |
Source: CSBS 2025/26 data tables, Table 4. Bases: 580 micro, 241 small, 154 medium, 76 large businesses.
- Among businesses with no cyber cover, 39% were not aware of cyber insurance, 34% said it was not a budget priority, 27% said leadership was not interested and 19% said it was too expensive (CSBS 2025/26).
- In DSIT’s separate study of 104 SMEs with 10 to 249 staff, 65% had cyber insurance. Of the 35% without it, 36% said cost was prohibitive, 31% said broker advice was unclear or limited and 28% did not think it necessary (DSIT, Insuring Resilience, August 2025; small sample, indicative).
- 59% of the insured SMEs in that study bought limits of up to £1 million at a median annual premium of £11,500, rising to a median of £55,000 for broader cover including business interruption, extortion and data breach. 65% had to meet specific security requirements to qualify and half of those spent between £5,000 and £25,000 to comply (DSIT, Insuring Resilience, 2025).
- BIBA quoted the same DSIT finding, that 35% of SMEs have no cyber insurance, when it launched its cyber broker directory in January 2026, and added Broker Insights research putting standalone cyber cover at under 3% of UK businesses (BIBA, 14 January 2026).
- 52% of businesses with cyber insurance say they would inform their insurer after a breach (CSBS 2025/26).
- Organisations certified to Cyber Essentials with turnover under £20 million receive £25,000 of cyber liability insurance at no extra cost, underwritten by AIG, with a £1,000 excess. It covers liability, event management, extortion, regulatory investigation and network interruption, and excludes money stolen by cyber fraud (IASME, 2026).
Have a think about the “do not know” column. A quarter of small businesses cannot say whether they are covered, and the person answering was the one the business named as most responsible for cyber security. The full UK picture on claims, payouts and premiums is on our cyber insurance statistics page.
6. Cyber Essentials and small businesses
Cyber Essentials is the government-backed baseline, and the only scheme that is priced for a ten-person firm.
- 5% of UK businesses hold Cyber Essentials, up from 3% in 2024/25. Among small businesses the figure doubled from 5% to 12%, and among large businesses it rose from 21% to 35%. 2% of businesses hold Cyber Essentials Plus (CSBS 2025/26).
- Among micro businesses that had heard of the scheme, 23% said they adhered to it, against 47% of small businesses that had heard of it (CSBS 2025/26 data tables, Table 10).
- Awareness is the bottleneck: 14% of micro and 25% of small businesses have heard of Cyber Essentials, against 56% of medium and 64% of large businesses (CSBS 2025/26).
- Micro and small organisations made up 69% of all Cyber Essentials certificates issued in 2022/23 (35% micro, 34% small), but that was only 0.2% of UK micro businesses and 3.8% of small businesses, against 12.6% of medium and 30.8% of large businesses (DSIT Cyber Essentials impact evaluation, October 2024).
- 66% of micro businesses with Cyber Essentials use no other scheme or standard; it is their only external assurance (DSIT impact evaluation, 2024).
- 39,790 Cyber Essentials and 12,850 Cyber Essentials Plus certificates were issued in the year to August 2025, both up about 17% (NCSC Annual Review 2025).
- Organisations with Cyber Essentials are 92% less likely to make a claim on their cyber insurance, according to the scheme’s bundled insurer (NCSC Annual Review 2025; one insurer’s book, no published methodology).
- Cyber Essentials self-assessment costs £320 plus VAT for a micro business and £440 plus VAT for a small business (IASME, 2026).
- 3% of businesses require their suppliers to hold Cyber Essentials, rising to 26% of large businesses, up from 10% a year earlier (CSBS 2025/26). That is the number that turns a small supplier’s certification from optional to required.
Suggested Read: Cyber Essentials Certification
7. What the numbers look like for a typical small firm
Put the CSBS findings together and the median UK small business in 2025/26 looks like this. It has about a dozen staff and no IT person; the office manager handles cyber security. It had phishing emails in the last year and nothing else it noticed, and the most disruptive incident cost it no money, only the time spent working out whether an email was real. It has antivirus, a firewall and cloud backups. It does not patch within 14 days as a rule, has no incident response plan, has not done a risk assessment, has not trained staff, has cyber cover buried in a wider policy with a sub-limit nobody has read, and has not heard of Cyber Essentials.
The tail is where the cost sits. One in five breached businesses had a material outcome, and for those the 95th percentile cost was around £14,000 in survey terms. In insurer terms an SME claim in EMEA now averages over $80,000, and City of London Police recorded 175 SME ransomware reports in a year with an average reported loss that the force itself says is understated. In our penetration testing work for small firms the finding that most often turns a phishing email into one of those claims is a single account without MFA, usually a shared mailbox or a remote access login that was set up years ago and never reviewed. The size table above says that account exists in more than half of micro businesses.

8. How small businesses can protect themselves on a limited budget
The NCSC’s Small Business Guide, republished in April 2026, is written for organisations with 0 to 49 staff and no technical expertise, and its five steps map directly onto the five Cyber Essentials controls. They are the controls the data in section 4 says small firms are missing, and none of them needs new software.
- Patch within 14 days and turn on automatic updates. Only 32% of micro and 39% of small businesses have a 14-day policy (CSBS 2025/26). Unpatched edge devices were the way in for 29% of the opportunistic ransomware cases in the Verizon data. Our guide to patch management covers how to do it without a dedicated IT team.
- Turn on multi-factor authentication everywhere it is offered, starting with email, cloud storage, accounting software and any remote access. 43% of micro businesses have it (CSBS 2025/26). Compromised credentials were the entry route in 38% of the Verizon ransomware cases, and the included Cyber Essentials insurance is conditional on controls like this being in place.
- Use the firewall and secure configuration you already own. Change default passwords, remove accounts and software nobody uses, and restrict admin rights; 31% of micro businesses do not restrict admin rights today (CSBS 2025/26).
- Keep malware protection on and up to date on every device, including personal phones that read company email. 20% of micro businesses do not (CSBS 2025/26).
- Back up, and test a restore. Cloud backup is the control small firms are best at (73% of micro, 80% of small), but 69% of the Verizon ransomware victims who refused to pay could do so because their backups worked. Test one restore a quarter.
Then two things that cost time rather than money. First, write a one-page incident plan: who to call, what to switch off, when to tell the ICO, the bank and the insurer. 48% of micro businesses have none of those things written down. Second, run the NCSC’s free Cyber Action Toolkit, launched in public beta in October 2025 for sole traders, micro and small businesses, which turns the same steps into a checklist and leads towards Cyber Essentials.
Cyber Essentials itself is the obvious next step once the five controls are in place. It costs £320 plus VAT for a micro business and £440 plus VAT for a small one, 26% of large businesses now ask their suppliers for it, and for firms with turnover under £20 million the certificate carries £25,000 of cyber liability insurance at no extra cost, which for an uninsured micro business is the cheapest cyber cover available in the UK.
Suggested Read: Cyber Essentials Certification Cost
Frequently asked questions
What percentage of cyber attacks target small businesses?
No UK source measures the share of all attacks aimed at small businesses, and the widely quoted figure of 43% comes from a 2019 vendor report. What the UK data does measure is prevalence: 42% of micro and 46% of small businesses identified a breach or attack in the last year, and 17% of micro and 24% of small businesses were victims of a cyber crime (CSBS 2025/26). Globally, about 96% of the ransomware victims in the Verizon DBIR 2026 were organisations with fewer than 1,000 staff.
How many UK small businesses were hit by a cyber attack in 2025?
Applying the CSBS 2025/26 rates to the business population, roughly 480,000 of the 1.15 million micro businesses and 100,000 of the 220,000 small businesses identified a breach or attack. DSIT’s own extrapolation for all businesses is 612,000. Hiscox found 38% of UK firms under 250 staff had suffered a successful attack by June 2026, the highest of any country it surveyed.
What is the most common cyber attack on small businesses?
Phishing, by a distance. 37% of micro and 40% of small businesses received phishing attacks in the last year, 70% of breached micro businesses said it was their most disruptive incident, and phishing made up 93% of cyber crimes against businesses (CSBS 2025/26). Impersonation (10% micro, 17% small) and malware (7%) are next.
How much does a cyber attack cost a small business in the UK?
The median cost of the most disruptive breach for micro and small businesses was £0, because most identified breaches are phishing emails that go nowhere. Where the breach had a material outcome the median was £560 and the top 5% cost £14,440 or more (CSBS 2025/26). Insurer data shows the other end: Chubb’s average EMEA SME claim was $82,621 in 2025 and Coalition’s average claim across all sizes was about £87,000.
What percentage of small businesses close after a cyber attack?
There is no reliable figure. The claim that most small businesses close within six months of an attack has no traceable primary source and has been withdrawn by the organisations once credited with it. The UK survey data says 5% of breached businesses lost revenue or share value and 3% suffered reputational damage (CSBS 2025/26), and Hiscox found 30% of attacked firms under 250 staff reported a negative effect on financial performance, valuation or credit rating.
Do small businesses need cyber insurance?
45% of micro and 55% of small UK businesses have some form of cyber cover, but only 8% and 15% hold a specific policy, and 33% of micro businesses have none (CSBS 2025/26). Cover inside a general policy usually carries a small sub-limit. Cyber Essentials certification includes £25,000 of cover for firms under £20 million turnover, and SMEs buying standalone cover in DSIT’s 2025 study paid a median of £11,500 for limits up to £1 million.
About this data
This page draws on reports published between October 2024 and September 2026. The UK prevalence, attack type, cost, control, governance, insurance and Cyber Essentials figures are from the DSIT Cyber Security Breaches Survey 2025/26 (fieldwork autumn 2025, published 30 April 2026) and its accompanying data tables; where we quote a figure by business size that does not appear in the report text, we have taken it from the published tables and named the table. Trend figures are from the 2024 and 2025 editions. Business counts are from the Department for Business and Trade’s Business Population Estimates 2025. Ransomware reporting is from City of London Police. SME insurance figures are from DSIT’s Insuring Resilience study (104 respondents, indicative) and BIBA. Cyber Essentials data is from the NCSC Annual Review 2025, DSIT’s 2024 impact evaluation and IASME. Hiscox figures are from the 2026 Cyber Readiness Report of 6,800 organisations with fewer than 250 staff in eleven countries. Chubb and Coalition figures are from their 2026 claims reports and cover EMEA and five countries respectively. Verizon DBIR figures are global and use Verizon’s definition of small business as under 1,000 employees. FSB figures are from its 2023 member survey, the most recent it has published, and are included only as a baseline.
Older figures from 2019 to 2022 that appeared in previous versions of this page, including US and multi-country vendor surveys, have been removed. We refresh this page after each Cyber Security Breaches Survey (April), the City of London Police ransomware release (June), the Hiscox report (September) and the Business Population Estimates (October).
If you cite a figure from this page, please link to the original source as well as to us; the references are below.
References
- DSIT, Cyber Security Breaches Survey 2025/26 (30 April 2026)
- DSIT, Cyber Security Breaches Survey 2025/26 data tables (ODS)
- DSIT, Cyber Security Breaches Survey 2025 (April 2025)
- DSIT, Cyber Security Breaches Survey 2024 (April 2024)
- Department for Business and Trade, Business Population Estimates 2025 (2 October 2025)
- Hiscox, Cyber Readiness Report 2026 (September 2026)
- City of London Police, ransomware warning (29 June 2026)
- Verizon, 2026 Data Breach Investigations Report
- DSIT, Summary of research on the economic impact of cyber attacks (12 November 2025)
- FSB, Cracking the Case: uncovering the cost of small business crime (2024, 2023 survey data)
- Chubb, EMEA Cyber Claims Report 2026
- Coalition, 2026 Cyber Claims Report, UK announcement (6 March 2026)
- DSIT, Insuring Resilience: adoption of cyber insurance by UK SMEs (11 August 2025)
- BIBA, cyber insurance brokers directory release (14 January 2026)
- IASME, Cyber Essentials cyber liability insurance
- IASME, Cyber Essentials pricing
- DSIT, Cyber Essentials impact evaluation (23 October 2024)
- NCSC Annual Review 2025, empowering organisations (14 October 2025)
- NCSC, Small Business Guide: Cyber Security (9 April 2026)
- NCSC, Cyber Action Toolkit launch (14 October 2025)