Just over four in ten UK businesses identified a cyber attack or breach in the last year, and most of those were phishing. That is the headline from the government’s Cyber Security Breaches Survey 2025/26, published on 30 April 2026, and it has barely moved in two years. What has moved is the severity at the top end: the NCSC handled more than twice as many nationally significant incidents as the year before, and a single attack on Jaguar Land Rover was costed at £1.9 billion to the UK economy.
In this article we have pulled together the latest UK cyber security statistics from the bodies that actually hold the data: DSIT’s breaches survey, the NCSC Annual Review, the ICO’s incident dataset, Report Fraud and the City of London Police, the ONS crime survey, and DSIT’s own studies of the cyber sector and its skills. UK figures come first in every section. Where a figure is global or European we say so in the line, because most of the numbers that circulate on this topic are American and get quoted as if they applied here.
This is the hub page for our statistics cluster. Phishing, social engineering, malware, small business, healthcare, penetration testing and cyber insurance each have their own page, linked from the sections they belong to, and we have kept the figures here to the ones that describe the UK picture as a whole.
Key UK cyber security statistics for 2026 at a glance
- 43% of UK businesses (about 612,000) and 28% of charities (about 57,000) identified a cyber breach or attack in the last 12 months, rising to 65% of medium and 69% of large businesses (Cyber Security Breaches Survey 2025/26, DSIT, April 2026).
- Phishing was identified by 38% of all businesses and by 88% of those that had any breach; ransomware was identified by 1% of businesses, down from 3% in each of the two previous years (CSBS 2025/26).
- 19% of businesses that identified a breach had a negative outcome such as lost access, lost data or stolen money. The median cost of the most disruptive breach was £0; the top 5% of cases cost £4,000 or more, and £15,000 or more where the breach had a material outcome (CSBS 2025/26).
- 19% of businesses (about 267,000) were victims of a cyber crime, UK businesses experienced an estimated 5.19 million cyber crimes, and 3% (about 43,000) were victims of cyber-facilitated fraud (CSBS 2025/26).
- The NCSC handled 429 incidents between September 2024 and August 2025, of which 204 were nationally significant, up from 89, and 18 were highly significant (NCSC Annual Review 2025).
- Organisations reported 13,457 personal data breaches to the ICO in 2025, of which 3,153 were cyber incidents; phishing (1,526) and ransomware (617) were the leading cyber causes (our count of the ICO data security incident trends dataset, 2025).
- Only 24% of businesses have controls in all five Cyber Essentials areas, 47% use any form of two-factor authentication, 34% have a policy to patch within 14 days and 5% hold a Cyber Essentials certificate (CSBS 2025/26).
- 25% of businesses have a formal incident response plan, and only 40% of those that identified a breach reported it outside the organisation (CSBS 2025/26).
- 57% of UK businesses (about 808,000) have a basic technical cyber security skills gap, up from 49% a year earlier (DSIT, Cyber security skills in the UK labour market 2026).
- The UK cyber security sector has 2,603 firms, £14.7 billion of revenue and 69,600 full-time employees (DSIT, Cyber security sectoral analysis 2026).
1. How many UK businesses were attacked in 2025/26?
The Cyber Security Breaches Survey is the only official UK statistic on this question. DSIT and the Home Office commission it every year; the 2025/26 edition surveyed 2,112 businesses and 1,085 charities between August and December 2025. It counts breaches and attacks that organisations identified and were willing to report, so DSIT itself says the figures are likely to understate the true position.
- 43% of UK businesses and 28% of UK charities identified a cyber breach or attack in the last 12 months, about 612,000 businesses and 57,000 charities (CSBS 2025/26).
- By business size: 42% of micro businesses, 46% of small, 65% of medium and 69% of large businesses (CSBS 2025/26).
- By charity income: 22% of low-income charities, 39% of medium-income and 57% of high-income charities with £500,000 or more (CSBS 2025/26).
- By sector, information and communication (63%) and professional, scientific and technical businesses (54%) were the most likely to identify an attack; retail and wholesale (31%) and food and hospitality (33%) the least likely (CSBS 2025/26).
- Among those attacked, 29% of businesses and 26% of charities experienced an attack at least weekly; the charity figure rose from 18% in 2024/25 (CSBS 2025/26).
- The business figure was 43% in 2024/25 and 50% in 2023/24. DSIT describes the last two years as in line with each other, after a fall driven by micro and small businesses (CSBS 2025/26).
Breaches identified in the Cyber Security Breaches Survey, 2017 to 2026
| Survey year | Businesses identifying a breach or attack | Charities |
|---|---|---|
| 2017 | 46% | not surveyed |
| 2018 | 43% | 19% |
| 2019 | 32% | 22% |
| 2020 | 46% | 26% |
| 2021 | 39% | 26% |
| 2022 | 39% | 30% |
| 2023 | 32% | 24% |
| 2024 | 50% | 32% |
| 2024/25 | 43% | 30% |
| 2025/26 | 43% | 28% |
Source: DSIT and DCMS, Cyber Security Breaches Survey, each year’s main report. The question behind the headline figure was reworded in the 2024 survey, and DSIT says results from 2024 onwards cannot be compared directly with earlier years. Treat the table as two series: 2017 to 2023, and 2024 to 2026.
Suggested Read: Small Business Cyber Security Statistics
2. Types of cyber attack identified by UK organisations
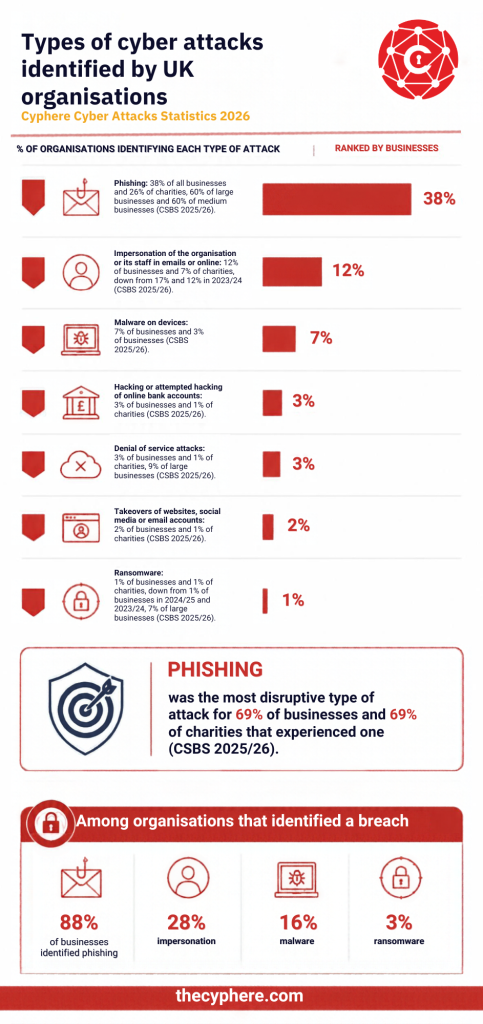
Phishing dominates every year, and the gap between it and everything else has widened. Among businesses that identified any breach, 51% identified phishing and nothing else, up from 45% a year earlier.
- Phishing: 38% of all businesses and 25% of charities; 63% of large businesses and 60% of medium businesses (CSBS 2025/26).
- Impersonation of the organisation or its staff in emails or online: 12% of businesses and 7% of charities, down from 17% and 12% in 2023/24 (CSBS 2025/26).
- Malware on devices: 7% of businesses and 3% of charities; 23% of large businesses (CSBS 2025/26).
- Hacking or attempted hacking of online bank accounts: 3% of businesses and 1% of charities (CSBS 2025/26).
- Denial of service attacks: 3% of businesses and 1% of charities; 9% of large businesses (CSBS 2025/26).
- Takeovers of websites, social media or email accounts: 2% of businesses and 1% of charities (CSBS 2025/26).
- Ransomware: 1% of businesses and 1% of charities, down from 3% of businesses in 2024/25 and 2023/24; 7% of large businesses (CSBS 2025/26).
- Among organisations that identified a breach, 88% of businesses identified phishing, 28% impersonation, 16% malware and 3% ransomware (CSBS 2025/26).
- Phishing was the most disruptive type of attack for 69% of businesses and 69% of charities that experienced one (CSBS 2025/26).
The ICO’s dataset tells a similar story from the other end, counting only incidents serious enough to be reported under UK GDPR: of the 3,153 cyber-related breaches reported in 2025, 1,526 were phishing, 770 other cyber incidents, 617 ransomware, 102 malware, 90 unauthorised access and 45 brute force (our count of the ICO dataset). Ransomware reports to the ICO have fallen for two years running, from 1,253 in 2023 to 752 in 2024 and 617 in 2025.
Should you feel you need to learn about these terms or more cyber linked glossary, terms and definitions, here’s our A-Z glossary of cyber.
Suggested Read: Phishing Statistics
Suggested Read: Malware Statistics
3. What cyber attacks cost UK businesses
DSIT changed how it reports cost this year. It no longer publishes a mean figure, on the grounds that a handful of very expensive incidents distort it, and instead reports the median and the 90th and 95th percentiles. That makes the headline look smaller than it used to, and it is more honest: most identified attacks are phishing emails that cost nothing, and the cost sits in a minority of cases.
- 19% of businesses and 11% of charities that identified a breach experienced a negative outcome, compared with 16% of both in 2024/25 (CSBS 2025/26).
- The most common outcomes for businesses were temporary loss of access to files or networks (8%), websites or online services taken down or slowed (6%), loss of access to third-party services (5%), money stolen (3%) and data altered, destroyed or taken (2%). 2% paid a ransom (CSBS 2025/26).
- 30% of businesses that identified a breach reported a wider impact, most commonly new protective measures (19%) and extra staff time (16%). 5% reported a loss of revenue or share value, up from 2%, and 3% reputational damage, up from 1% (CSBS 2025/26).
- 87% of businesses restored operations within a day of their most disruptive breach, down from 92% in each of the two previous years (CSBS 2025/26).
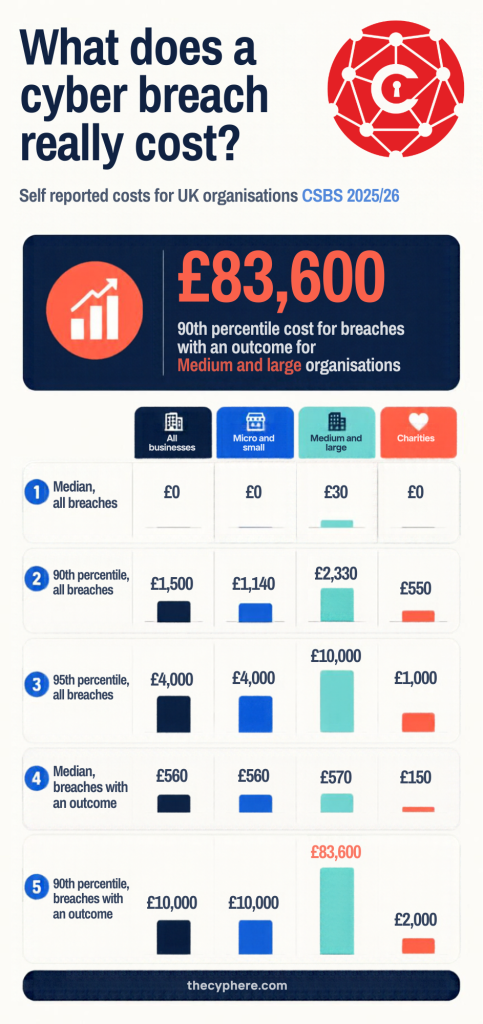
- Median perceived cost of the most disruptive breach: £0 for businesses overall, £30 for medium and large businesses, £0 for charities (CSBS 2025/26).
- Where the breach had a material outcome, the median rose to £560 for businesses and the top 5% of cases to £15,000; the top 10% of medium and large businesses with an outcome faced £83,600 or more (CSBS 2025/26).
- Excluding organisations that reported a £0 cost, the top 5% of medium and large businesses faced £28,200 or more (CSBS 2025/26).
- For comparison, the last mean figures DSIT published were for 2024/25: £1,600 per business for the most disruptive breach, and £8,260 among businesses that experienced an outcome (CSBS 2024/25).
Cost of the most disruptive breach, UK businesses, 2025/26
| Measure | All businesses | Micro and small | Medium and large | Charities |
|---|---|---|---|---|
| Median, all breaches | £0 | £0 | £30 | £0 |
| 90th percentile, all breaches | £1,500 | £1,140 | £2,330 | £550 |
| 95th percentile, all breaches | £4,000 | £4,000 | £10,000 | £1,000 |
| Median, breaches with an outcome | £560 | £560 | £570 | £150 |
| 90th percentile, breaches with an outcome | £10,000 | £10,000 | £83,600 | £2,000 |
Source: CSBS 2025/26, Tables 4.1a and 4.1b. Costs are self-reported.
Our view is that the survey’s cost figures describe the typical phishing email, not the incident that puts a company in the news. The £1.9 billion JLR estimate in section 11 and the £300 million M&S profit warning are the other end of the same distribution, and neither would show up in a survey median.
Suggested Read: Cyber Insurance Statistics
4. Boards, governance and risk management
- Cyber security is a high priority for senior management in 72% of businesses and 60% of charities. The charity figure fell from 68%, driven by low-income charities (CSBS 2025/26).
- 31% of businesses and 30% of charities have a board member or trustee with explicit responsibility for cyber security. The business figure rose from 27% in 2024/25, reversing a decline that ran from 2020/21 (CSBS 2025/26).
- Board responsibility by size: 29% of micro, 37% of small, 52% of medium and 68% of large businesses. Finance and insurance (54%) and information and communication (51%) lead; transport and storage (17%) and retail and wholesale (20%) trail (CSBS 2025/26).
- 30% of businesses and 27% of charities carried out a risk assessment covering cyber security; 32% of businesses use security monitoring tools, 18% ran a vulnerability audit and 13% commissioned a penetration test (CSBS 2025/26).
- 36% of businesses have a formal cyber security policy and 33% a business continuity plan that covers cyber. Among small businesses both fell back: policy 52% (from 59%), continuity plan 44% (from 53%) (CSBS 2025/26).
- 47% of businesses and 35% of charities have some form of cyber insurance, but only 10% of businesses hold a specific cyber policy and 22% do not know whether they are covered (CSBS 2025/26).
- 31% of businesses are using, adopting or considering AI; of those, 24% have cyber security practices in place for the risks that come with it (CSBS 2025/26).
- 14% of businesses and 22% of charities hold personal data that is not protected by anonymisation or encryption (CSBS 2025/26).
The insurance figures are covered in depth on our cyber insurance statistics page, including claims, payouts and what insurers now ask for.
Suggested Read: Penetration Testing Statistics
5. Which security controls UK businesses actually have in place
The survey measures the five Cyber Essentials control areas directly: firewalls, secure configuration of company-owned devices, restricted admin rights, malware protection and patching within 14 days. Awareness of the scheme is low, but the controls are more common than the certificate.
- Up-to-date malware protection: 81% of businesses (77% in 2024/25) and 63% of charities (CSBS 2025/26).
- Network firewalls covering the network and devices: 74% of businesses and 45% of charities (CSBS 2025/26).
- Restricted admin and access rights: 73% of businesses (68% in 2024/25) and 65% of charities (CSBS 2025/26).
- Security controls on company-owned devices: 61% of businesses and 42% of charities (CSBS 2025/26).
- A policy to apply software security updates within 14 days: 34% of businesses and 20% of charities, the weakest of the five areas by a distance (CSBS 2025/26).
- All five Cyber Essentials control areas in place: 24% of businesses and 13% of charities, up from 21% and 12% in 2024/25 but below the 29% and 20% recorded in 2020/21. 51% of medium and 70% of large businesses have all five (CSBS 2025/26).
- Any two-factor authentication: 47% of businesses (40% in 2024/25) and 38% of charities; 43% of micro businesses (35%) and 90% of large businesses (CSBS 2025/26).
- Secure cloud backup: 74% of businesses (71%) and 57% of charities; other backups 48% and 38% (CSBS 2025/26).
- Password policies 74% of businesses; VPN for remote staff 36% (31%); separate staff and guest Wi-Fi 38%; monitoring of user activity 33% (CSBS 2025/26).
- 17% of businesses and 16% of charities are aware of Cyber Essentials when prompted. 5% of businesses hold Cyber Essentials, up from 3%, and 2% hold Cyber Essentials Plus; among large businesses, 35% hold Cyber Essentials (21% in 2024/25) and 12% hold Plus (CSBS 2025/26).
- 39,790 Cyber Essentials and 12,850 Cyber Essentials Plus certificates were issued in the year to August 2025, up 17.5% and 17.3%, through 402 certification bodies (NCSC Annual Review 2025).
- 48% of businesses and 25% of charities have an external cyber security provider; among micro businesses the figure rose from 39% to 44% (CSBS 2025/26).
In our Cyber Essentials Plus audits and penetration tests, the control a business reports in a survey and the control we find on the network are often two different things. Multi-factor authentication is enforced on Microsoft 365 but not on the legacy VPN appliance; the 14-day patching policy exists on paper but the firewall firmware and the one server that cannot be rebooted are months behind; admin rights are restricted for staff but the local administrator password is the same on every laptop. The 34% patching figure above is self-reported, and we would expect an audited figure to be lower. A gap means a risk not yet assessed or measured, which is the point of having the audit done.
Suggested Read: Cyber Essentials Benefits
6. Supply chain risk
Supply chain compromise was the most common initial attack vector in IBM’s UK breach sample (section 12), and the JLR incident in section 11 was felt mainly through its suppliers. The survey shows how few UK organisations look at this risk formally.
- 15% of businesses and 9% of charities reviewed the cyber security risks posed by their immediate suppliers in the last year; 6% and 4% reviewed their wider supply chain (CSBS 2025/26).
- By size: 12% of micro, 22% of small, 30% of medium and 48% of large businesses reviewed immediate suppliers (CSBS 2025/26).
- 22% of businesses consider cyber security to a large extent when buying software, rising to 54% of medium and 69% of large businesses (CSBS 2025/26).
- 47% of businesses said they would inform their immediate suppliers or wider supply chain after a breach (CSBS 2025/26).
Since February 2025, central government, its agencies and NHS bodies have been required under PPN 014 to ask suppliers on higher-risk contracts for Cyber Essentials or equivalent controls, which is one reason the certificate counts in section 5 are growing faster than the survey’s adoption figures.
7. Incident response and reporting
- 25% of businesses and 19% of charities have a formal incident response plan: 21% of micro, 57% of medium and 76% of large businesses, and 53% of finance and insurance businesses (CSBS 2025/26).
- 39% of businesses have assigned incident roles, 34% have written guidance on who to notify and 32% have guidance on when to report externally. 45% of businesses and 54% of charities have none of these measures (CSBS 2025/26).
- 49% of businesses and 34% of charities have a policy not to pay ransomware demands; 24% and 21% do not know what their policy is (CSBS 2025/26).
- After their most disruptive breach, 81% of businesses informed directors, 62% kept an internal record and 50% tried to identify the source. 16% would use an NCSC-assured incident response company (CSBS 2025/26).
- 40% of businesses and 36% of charities that identified a breach reported their most disruptive breach outside the organisation (CSBS 2025/26).
- Among businesses that reported beyond their IT provider, the most common destinations were their bank (26%), their internet or network provider (11%), another government agency (10%), Action Fraud (9%), the police (6%) and the ICO (2%). Less than 0.5% reported to the NCSC, down from 5% in 2023/24. Charities were far more likely to report to the ICO (16%) (CSBS 2025/26).
- 72% of businesses that did not report said the breach was not significant enough; 10% did not know who to report to (CSBS 2025/26).
- 61% of businesses took action after a breach, most commonly people or training changes (31%). Where the breach had a material outcome, 83% took action, but 14% still did nothing (CSBS 2025/26).
- 15% of cyber-related breach reports reached the ICO more than a week after the incident in 2025 (476 of 3,153), against the 72-hour UK GDPR deadline (our count of the ICO dataset).
- 47% of the people responsible for cyber security in UK businesses and charities are not confident they could deal with a breach, and 49% of business cyber leads are not confident writing an incident response plan (DSIT skills 2026).
Suggested Read: Cyber Security Incident Response Plan
8. UK cyber crime and fraud statistics
Cyber crime is a subset of the breaches above: the survey only counts an incident as a crime where it meets the Computer Misuse Act and Home Office counting rules. The police and ONS figures count reports and household survey estimates, so they measure different things and should not be added together.
- 19% of businesses (about 267,000) and 14% of charities (about 28,000) were victims of at least one cyber crime in the last 12 months. The trend is 22% in 2023/24, 20% in 2024/25 and 19% in 2025/26 (CSBS 2025/26).
- By size: 17% of micro, 24% of small, 41% of medium and 48% of large businesses (CSBS 2025/26).
- Phishing accounts for 93% of business cyber crime victims; 3% of all businesses experienced a non-phishing cyber crime (CSBS 2025/26).
- UK businesses experienced an estimated 5.19 million cyber crimes of all types in the last 12 months, including about 70,000 non-phishing cyber crimes; charities about 525,000 (CSBS 2025/26).
- The median business that experienced cyber crime had three incidents; the mean was 19, which points to repeat victimisation of a minority (CSBS 2025/26).
- Median cost of a non-phishing cyber crime: £250 including £0 responses, £750 excluding them; the top 10% of cases cost £5,000 or more (CSBS 2025/26).
- 3% of businesses (about 43,000) and 1% of charities were victims of cyber-facilitated fraud, an estimated 130,000 fraud events. The median cost was £110, or £500 among those with a cost, and the top 10% of cases cost £12,000 or more (CSBS 2025/26).
- 323 organisations reported a ransomware attack to Report Fraud between April 2025 and March 2026, 175 of them SMEs, with reported losses of about £270,000, up 50% on the previous year. Manufacturing (42), scientific and technical (21) and education (19) reported most (City of London Police, June 2026).
- Report Fraud, which replaced Action Fraud in January 2026, recorded a 395% rise in AI-related fraud reports in 2025/26, from 193 to 956, with losses up from £1.2 million to £9.6 million (City of London Police, September 2026).
- The Crime Survey for England and Wales estimated 798,000 computer misuse incidents against individuals in the year ending March 2026, with no statistically significant change on the previous year, and 4.5 million fraud incidents (ONS, July 2026).
Suggested Read: Social Engineering Statistics
9. Training, skills and the UK cyber security workforce
- 19% of businesses and 17% of charities ran cyber security training or awareness sessions in the last year: 14% of micro, 33% of small, 54% of medium and 84% of large businesses (CSBS 2025/26).
- 22% of businesses and 13% of charities tested staff with mock phishing or similar exercises (CSBS 2025/26).
- 57% of UK businesses, about 808,000, have a basic technical cyber security skills gap, meaning the person responsible is not confident in at least one basic task such as configuring a firewall or removing malware. That is up from 49% (about 699,000) in 2025. The gap is 24% for large businesses and 58% for charities (DSIT skills 2026).
- The widest basic gaps are in detecting and removing malware (38% of businesses not confident, up from 23%) and storing and transferring personal data securely (31%, up from 25%) (DSIT skills 2026).
- 27% of businesses (about 383,000) have an advanced skills gap; 19% are not confident carrying out penetration testing and 20% forensic analysis (DSIT skills 2026).
- The UK cyber security workforce is about 145,900 people, up 2% in a year, down from 5% growth the year before. DSIT estimates the sector needs about 10,200 new entrants a year, 4,400 for growth and 5,800 to replace leavers (DSIT skills 2026).
- Core cyber job postings rose 7% in 2025 to 34,932; Greater London, Manchester, Birmingham and Bristol are the top four locations (DSIT skills 2026).
- 16% of the cyber workforce is female and 9% disabled, against 48% and 18% of the UK workforce (DSIT skills 2026).
- Cyber security graduates rose 14% to 7,950, while enrolments on cyber apprenticeships fell 15% (DSIT skills 2026).
- The UK cyber security sector has 2,603 firms, up 20%, with revenue of £14.7 billion (up 11%), gross value added of about £9.1 billion (up 17%) and 69,600 full-time equivalent employees (up 3%). Firms raised £184 million across 47 investment deals in 2025 (DSIT sectoral analysis 2026).
10. The UK threat picture: NCSC and ICO figures
- The NCSC received 1,727 incident tips between September 2024 and August 2025 and triaged them into 429 incidents requiring its support, a similar total to the previous year (NCSC Annual Review 2025).
- 204 of those incidents (48%) were nationally significant, up from 89 the year before; 18 (4%) were highly significant, a 50% rise and the third consecutive annual increase (NCSC Annual Review 2025).
- Nationally significant incidents by year: 63 (2021/22), 62 (2022/23), 89 (2023/24), 204 (2024/25) (NCSC Annual Review 2025).
- The sectors reporting most ransomware activity to the NCSC were academia, finance, engineering, retail and manufacturing (NCSC Annual Review 2025).
- Three vulnerabilities, in Microsoft SharePoint Server (CVE-2025-53770), Ivanti Connect Secure (CVE-2025-0282) and Fortinet FortiManager (CVE-2024-47575), were linked to 29 incidents the NCSC managed (NCSC Annual Review 2025).
- The NCSC’s Takedown Service removed 1.2 million cyber-enabled commodity campaigns and disrupted more than 26,000 phishing campaigns targeting government departments; the Suspicious Email Reporting Service received over 10.9 million reports in the year (NCSC Annual Review 2025).
- Organisations reported 13,457 personal data breaches to the ICO in 2025, up from 12,194 in 2024 and 11,069 in 2023. 3,153 were cyber incidents, against 3,116 in 2024 and 3,319 in 2023 (our count of the ICO dataset, Q1 2019 to Q4 2025).
- Retail and manufacturing reported the most cyber breaches to the ICO in 2025 (805), followed by finance, insurance and credit (400), transport and leisure (284), education and childcare (259) and charities (229). Across all breach types, health (2,471) and education (1,830) reported most (our count of the ICO dataset).
- Non-cyber causes still outnumber cyber ones at the ICO by more than three to one: data emailed to the wrong recipient (2,459) was the single largest category in 2025 (our count of the ICO dataset).
Suggested Read: Healthcare Cyber Attack Statistics

11. Recent UK examples, 2025 to 2026
These are the incidents that moved the NCSC’s nationally significant count and the public’s perception of the risk. Each figure is from the organisation’s own statement or from the Cyber Monitoring Centre, the independent body that categorises UK cyber events.
- Jaguar Land Rover, September 2025. Vehicle production stopped across JLR’s UK plants for about five weeks after an attack in late August. The Cyber Monitoring Centre categorised it as a Category 3 systemic event and modelled the cost to the UK economy at £1.9 billion (range £1.6 billion to £2.1 billion), with more than 5,000 UK organisations affected and most of the loss falling on halted manufacturing at JLR and its suppliers. The CMC called it the most economically damaging cyber event to hit the UK (Cyber Monitoring Centre, 22 October 2025).
- Marks and Spencer and Co-op, April to June 2025. M&S disclosed its attack on 22 April 2025 and on 21 May told investors it expected a hit of about £300 million to 2025/26 operating profit, with online fashion, home and beauty sales offline until July (M&S results statement, 21 May 2025). The Cyber Monitoring Centre assessed the M&S and Co-op incidents together as a Category 2 systemic event with a combined financial impact of £270 million to £440 million (Cyber Monitoring Centre, June 2025).
The common thread in the survey’s qualitative interviews was that these cases, not government guidance, were what moved cyber security up the board agenda in 2025. One large business told DSIT its board’s risk appetite had “descended” because of “the building cadence of catastrophic stories”.
12. Global context
A short section, because global figures get over-quoted in UK articles. Three sources with published methodology:
- The global average cost of a data breach reached a record $4.99 million in 2026, and the UK average was £3.13 million, down from £3.29 million; 22% of UK organisations reported AI-generated attacks (IBM Cost of a Data Breach Report 2026, UK findings, July 2026). In the previous year’s UK sample, supply chain compromise (18%), phishing (16%) and compromised credentials (11%) were the leading initial attack vectors, UK financial services breaches averaged £5.74 million, and UK organisations using AI and automation extensively in security took 148 days to identify and 42 to contain a breach, against 168 and 64 days for those that did not (IBM Cost of a Data Breach Report 2025, July 2025).
- 31% of breaches now start with the exploitation of a software vulnerability, and ransomware was present in 48% of all breaches analysed (Verizon 2026 Data Breach Investigations Report, global).
- ENISA analysed 4,875 incidents affecting the EU between July 2024 and June 2025. DDoS was 77% of reported incidents, almost all low-impact hacktivism; phishing was the initial intrusion vector in about 60% of cases and vulnerability exploitation in 21.3%; public administration was the most targeted sector at 38.2% (ENISA Threat Landscape 2025, October 2025).
13. UK cyber security law and regulation: what changed in 2025 and 2026
Statistics pages rarely cover this, and it is the context most readers are missing. The table shows the position as at 11 October 2026.
| Measure | Status | What it means for UK organisations |
|---|---|---|
| Cyber Security and Resilience Bill | Introduced in the Commons 12 November 2025; Commons third reading 16 June 2026; Lords second reading 14 July 2026; Lords committee stage from 1 September 2026; Lords report stage listed for 26 October 2026. No Royal Assent as at 11 October 2026 (UK Parliament) | Updates the NIS Regulations 2018: brings managed service providers and data centres into scope, widens incident reporting and strengthens regulators’ powers |
| Data (Use and Access) Act 2025 | Royal Assent 19 June 2025. Main data protection provisions in force 5 February 2026 under SI 2026/82, including recognised legitimate interests, DSAR time limits and PECR fines at UK GDPR levels; complaints provisions 19 June 2026; the Information Commission replaced the Information Commissioner on 30 September 2026 under SI 2026/1015 (legislation.gov.uk) | The ICO’s successor has UK GDPR-level fining powers for PECR breaches, and organisations must have a process for handling data subject complaints |
| PPN 014: Cyber Essentials in public procurement | Published 17 February 2025, in effect for procurements from 24 February 2025 (Cabinet Office) | Central government, agencies and NHS bodies must require Cyber Essentials, Cyber Essentials Plus or equivalent controls from suppliers on higher-risk contracts, renewed annually |
| Ransomware payment ban | Government response to the Home Office consultation published 22 July 2025: a targeted ban on ransom payments by public sector bodies and critical national infrastructure operators confirmed; a payment prevention regime and mandatory reporting still being developed (Home Office) | Public bodies and CNI operators will be prohibited from paying; private businesses would have to notify before paying once the prevention regime is legislated |
| NCSC Cyber Assessment Framework v4.0 | Published 6 August 2025 (NCSC) | Adds attacker-methods and secure software development sections and AI-related risk coverage; the framework used by NIS regulators and expected to underpin the Bill |
Frequently asked questions
What percentage of UK businesses experienced a cyber attack in 2026?
43% of UK businesses and 28% of charities identified a cyber breach or attack in the 12 months before the survey, about 612,000 businesses. The rate rises to 65% of medium and 69% of large businesses (Cyber Security Breaches Survey 2025/26).
What is the most common type of cyber attack in the UK?
Phishing. 38% of all UK businesses identified phishing in the last year, and 88% of businesses that identified any breach identified phishing. Impersonation (12%) and malware (7%) are a distant second and third. Ransomware was identified by 1% of businesses (CSBS 2025/26).
How much does a cyber attack cost a UK business?
For most businesses, nothing: the median cost of the most disruptive breach was £0. Where the breach had a material outcome, the median was £560 and the top 5% of cases cost £15,000 or more; the top 10% of medium and large businesses with an outcome faced £83,600 or more. The last mean figure DSIT published was £1,600 per business in 2024/25 (CSBS 2025/26 and 2024/25).
How many cyber crimes are there in the UK each year?
DSIT estimates UK businesses experienced about 5.19 million cyber crimes in the last 12 months, with 19% of businesses (about 267,000) victims of at least one. Separately, the Crime Survey for England and Wales estimated 798,000 computer misuse incidents against individuals in the year to March 2026 (CSBS 2025/26; ONS, July 2026).
How many UK businesses have Cyber Essentials?
5% of UK businesses hold Cyber Essentials and 2% hold Cyber Essentials Plus, rising to 35% and 12% of large businesses. 24% of businesses have controls in all five Cyber Essentials areas. 39,790 Cyber Essentials and 12,850 Plus certificates were issued in the year to August 2025 (CSBS 2025/26; NCSC Annual Review 2025).
What is the Cyber Security Breaches Survey?
An official statistic commissioned by DSIT and the Home Office and run by Ipsos. The 2025/26 edition surveyed 2,112 UK businesses, 1,085 charities and 577 education institutions between August and December 2025 and was published on 30 April 2026. It is the primary source for most UK cyber security statistics, including every DSIT figure on this page.
About this data
This page draws on reports published between July 2025 and September 2026. The UK prevalence, attack type, cost, governance, controls, incident response and cyber crime figures are from the DSIT Cyber Security Breaches Survey 2025/26 (fieldwork August to December 2025, published 30 April 2026), with comparisons to the 2024/25 and 2023/24 editions only where DSIT reports a trend. The trend table from 2017 uses each year’s main report and carries DSIT’s own caveat about the 2024 question change. Threat figures are from the NCSC Annual Review 2025 (covering September 2024 to August 2025). ICO figures are our own count of unique incident references in the ICO’s published data security incident trends dataset (Q1 2019 to Q4 2025); we count each reference once regardless of how many data types or subject categories it lists. Police figures are from City of London Police releases. Skills and sector figures are from DSIT’s Cyber security skills in the UK labour market 2026 and Cyber security sectoral analysis 2026. Incident costs are from the Cyber Monitoring Centre and the companies’ own statements. Global figures are from IBM, Verizon and ENISA and are labelled as such.
All figures from the 2017 to 2021 editions of the survey that appeared in previous versions of this page, and all US and global aggregator figures, have been removed. We refresh this page after each Cyber Security Breaches Survey (April), each NCSC Annual Review (October) and each ICO quarterly data release.
If you cite a figure from this page, please link to the original source as well as to us; the references are below.
References
P.S: If you cite a figure from this page, please link to the original source as well as to us; the references are below.
- DSIT and Home Office, Cyber Security Breaches Survey 2025/26 (30 April 2026)
- DSIT, Cyber Security Breaches Survey 2025 (2024/25)
- DSIT, Cyber Security Breaches Survey 2024
- DSIT and DCMS, Cyber Security Breaches Survey collection (2017 to 2023 editions)
- NCSC Annual Review 2025 (14 October 2025)
- ICO, Data security incident trends dataset (Q1 2019 to Q4 2025)
- City of London Police, ransomware warning (29 June 2026)
- City of London Police, Report Fraud intelligence assessment (3 September 2026)
- ONS, Crime in England and Wales: year ending March 2026 (23 July 2026)
- DSIT, Cyber security skills in the UK labour market 2026 (29 September 2026)
- DSIT, Cyber security sectoral analysis 2026 (12 May 2026)
- Cyber Monitoring Centre, statement on the Jaguar Land Rover cyber incident (22 October 2025)
- Cyber Monitoring Centre, statement on ransomware incidents in the retail sector (June 2025)
- Marks and Spencer, full year results and cyber incident update (21 May 2025), via The Register
- IBM, Cost of a Data Breach Report 2026, UK findings (28 July 2026)
- IBM, Cost of a Data Breach Report 2025, UK findings (30 July 2025)
- Verizon, 2026 Data Breach Investigations Report
- ENISA, Threat Landscape 2025 (1 October 2025)
- UK Parliament, Cyber Security and Resilience Bill, stages
- The Data (Use and Access) Act 2025 (Commencement No. 6 and Transitional and Saving Provisions) Regulations 2026, SI 2026/82
- The Data (Use and Access) Act 2025 (Commencement No. 9 and Transitional and Saving Provisions) Regulations 2026, SI 2026/1015
- Cabinet Office, PPN 014: Cyber Essentials scheme (17 February 2025)
- Home Office, government response to ransomware legislative proposals (22 July 2025)
- NCSC, CAF v4.0 released in response to growing threat (6 August 2025)