Phishing is the attack type that reaches almost every UK organisation. It is the most common breach the government’s survey records, the most common cyber crime businesses report, the largest category of cyber breach reported to the ICO, and the route behind most of the payment diversion fraud that costs UK businesses over £100 million a year.
In this article we have pulled together the latest phishing statistics from the organisations that actually hold the data: the Cyber Security Breaches Survey, the NCSC, the ICO, Report Fraud (the service that replaced Action Fraud in January 2026), UK Finance and Ofcom for the UK, and the APWG, Verizon, Microsoft, the FBI and the insurers’ claims reports for the global picture. UK figures come first in every section. Where a figure is global or US-only we say so in the line, because most of the phishing numbers that circulate online are American and get quoted as if they applied here.
Key phishing statistics for 2026 at a glance
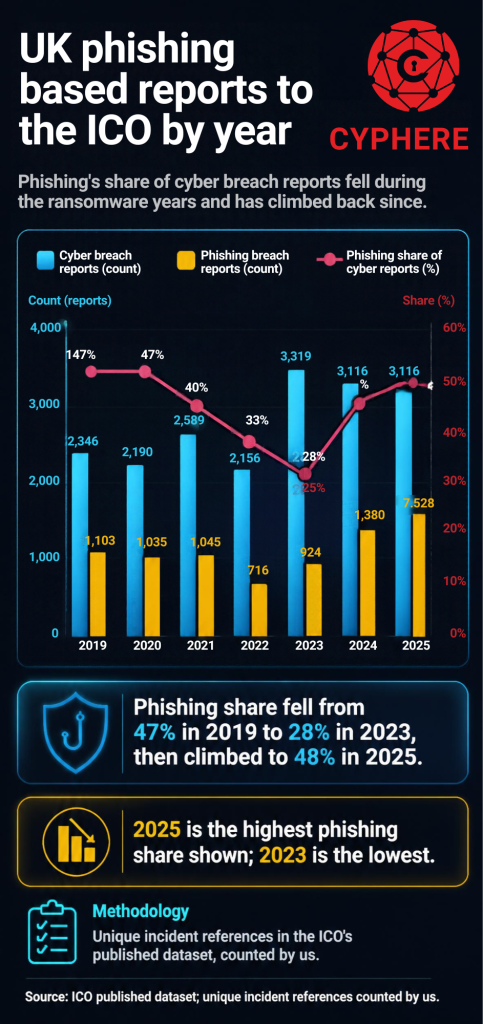
- 38% of UK businesses and 25% of UK charities experienced a phishing attack in the last 12 months, and phishing was the most disruptive attack type for 69% of those that had a breach (Cyber Security Breaches Survey 2025/26, DSIT, April 2026).
- Phishing made up 93% of the cyber crimes UK businesses experienced, out of an estimated 5.19 million cyber crimes in the year (CSBS 2025/26).
- The NCSC’s Suspicious Email Reporting Service received over 10.9 million reports in the year to August 2025, over 45 million since April 2020, and has removed 412,000 malicious URLs (NCSC Annual Review 2025).
- UK organisations reported 1,526 phishing-caused personal data breaches to the ICO in 2025, 48% of all cyber breach reports and up from 1,380 in 2024 (our count of the ICO data security incident trends dataset).
- Payment diversion fraud (business email compromise) cost UK victims £101 million across 3,657 reports in 2025/26 (Report Fraud Annual Assessment FY2025-26, City of London Police).
- Half of UK mobile users received a suspicious text between November 2024 and February 2025, and around 100 million suspicious messages were reported to 7726 in the year to April 2025 (Ofcom, October 2025).
- The APWG observed 3.8 million phishing attacks worldwide in 2025 and 1,069,681 in the second quarter of 2026; June 2026 was the busiest month since April 2023 (APWG Phishing Activity Trends Reports, global).
- Phishing was the initial access vector in 16% of breaches worldwide and 28% of breaches in Europe, the Middle East and Africa; the median click rate in email phishing simulations was 1.4% (Verizon DBIR 2026, global).
- Adversary-in-the-middle kits now account for 44.6% of identified phishing techniques, and 87.7% of phishing intrusions involved credential or session harvesting; Microsoft detected more than 145 million QR code phishing attacks and 46 million business contact impersonation attacks between July 2025 and June 2026 (Microsoft Digital Defense Report 2026, global).
- Phishing was the initial access vector in 11% of the intrusions Microsoft Defender Experts investigated, behind user execution (30%), valid accounts (20%) and ClickFix-style copy-and-paste attacks (13%); nearly 85% of reported phishing emails between April and June 2026 carried an impersonation signal (Microsoft Digital Defense Report 2026).
- Business email compromise cost US victims $3.05 billion across 24,768 complaints in 2025, and phishing and spoofing was the most reported crime type with 191,561 complaints (FBI IC3 2025 Internet Crime Report, US).
1. How common is phishing in the UK?
The best measure of how many UK organisations are hit is the Cyber Security Breaches Survey, which DSIT runs every year with around 2,000 businesses and 1,000 charities; the 2025/26 edition was published on 30 April 2026. The NCSC, the ICO and Report Fraud each count something different: reports from the public, breaches of personal data, and crimes with a loss.
- 43% of UK businesses (around 612,000) and 28% of charities (around 57,000) identified a cyber breach or attack in the last 12 months (CSBS 2025/26).
- 38% of businesses and 25% of charities experienced phishing, by far the most common type. The next most common, people impersonating the organisation in emails or online, was 12% for businesses and 7% for charities, and ransomware was 1% (CSBS 2025/26).
- Among organisations that had any breach, 51% of businesses and 57% of charities experienced phishing and nothing else, up from 45% and 46% the previous year (CSBS 2025/26).
- Phishing was the most disruptive breach or attack for 69% of businesses and charities that had one (CSBS 2025/26).
- 19% of businesses and 14% of charities were victims of at least one cyber crime; phishing accounted for 93% of business cyber crimes and 95% of charity cyber crimes, which is 18% of all businesses and 13% of all charities. DSIT estimates around 5.19 million cyber crimes against businesses in the year, of which only around 70,000 were not phishing (CSBS 2025/26).
- The NCSC’s Suspicious Email Reporting Service received over 10.9 million reports between September 2024 and August 2025 and over 45 million since it launched in April 2020, leading to the removal of 412,000 malicious URLs (NCSC Annual Review 2025).
- Organisations reported 13,457 personal data breaches to the ICO in 2025, of which 3,153 were cyber incidents and 1,526 were caused by phishing. Phishing was the largest cyber category, ahead of “other cyber incident” (770) and ransomware (617) (our count of the ICO dataset, Q1 2019 to Q4 2025).
- Phishing breach reports to the ICO rose every quarter of 2025: 328 in Q1, 363 in Q2, 406 in Q3 and 429 in Q4 (our count of the ICO dataset).
- Report Fraud received 64,608 cyber crime reports in 2025/26, up 34%, and phishing and social engineering were the most commonly reported attack vectors in the 2,271 cyber crime reports from organisations (Report Fraud Annual Assessment FY2025-26).
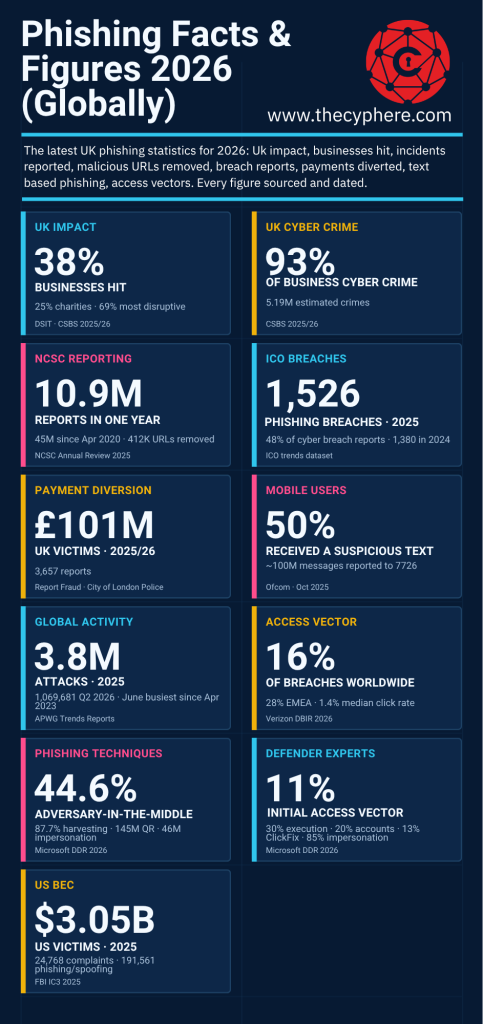
UK phishing breach reports to the ICO by year
Phishing’s share of cyber breach reports fell during the ransomware years and has climbed back since. These are unique incident references in the ICO’s published dataset, counted by us.
| Year | Cyber breach reports | Phishing breach reports | Phishing share of cyber reports |
|---|---|---|---|
| 2019 | 2,346 | 1,103 | 47% |
| 2020 | 2,190 | 1,035 | 47% |
| 2021 | 2,589 | 1,045 | 40% |
| 2022 | 2,156 | 716 | 33% |
| 2023 | 3,319 | 924 | 28% |
| 2024 | 3,116 | 1,380 | 44% |
| 2025 | 3,153 | 1,526 | 48% |
Our view is that the survey figure (38% of businesses) and the ICO figure (1,526 reports) are measuring different ends of the same problem. Most phishing never gets past the inbox, and the survey counts attempts. The ICO counts the cases where someone clicked, an account was taken over and personal data was exposed, which is roughly one in every 400 businesses that experienced phishing.
2. What percentage of cyber attacks and data breaches are phishing?
This is the question the page gets found for most, and the honest answer is that it depends on what is being counted. Surveys of organisations put phishing at the top because it is the attack everyone sees. Incident response and insurance data put it lower, because exploited vulnerabilities and stolen credentials cause more of the breaches that end in a claim.
- Phishing accounted for 93% of cyber crimes experienced by UK businesses and 95% of those experienced by charities (CSBS 2025/26).
- Phishing caused 48% of the cyber breaches reported to the ICO in 2025 and 11% of all 13,457 breach reports including non-cyber causes (our count of the ICO dataset).
- Among UK organisations hit by ransomware, malicious email (25%) and phishing (22%) together were the root cause of just under half of attacks; compromised credentials led at 28% and exploited vulnerabilities fell to 18% from 36% a year earlier (Sophos State of Ransomware in the UK 2026, 120 respondents, surveyed January to March 2026).
- Phishing was the third most common root cause of the incidents Pinsent Masons’ cyber team handled in 2025, at around 13%, behind exploitation of a vulnerability (21%) and unknown (19%); business email compromise was 17% of matters, down from 26% in 2024 (Pinsent Masons Cyber Annual Report 2026, UK).
- Phishing was the initial access vector in 16% of breaches worldwide, unchanged from the previous year, with pretexting at 6%. Exploitation of vulnerabilities (31%) overtook credential abuse (13%) as the leading vector (Verizon DBIR 2026, global).
- In Europe, the Middle East and Africa, phishing was the initial access vector in 28% of breaches and appeared in 84% of social-related breaches, against 69% across the whole dataset (Verizon DBIR 2026).
- The human element was present in 62% of breaches and social engineering was 16% of breaches (Verizon DBIR 2026); the social engineering statistics page covers the non-phishing side of that number.
- In the intrusions Microsoft Defender Experts investigated between July 2025 and June 2026, phishing was the initial access technique in 11% of cases (10.9%), behind user execution (30%), valid accounts (20%) and malicious copy-and-paste, the ClickFix pattern where a user is talked into pasting a command, at 13%. Drive-by compromise was 6% and exploitation of public-facing applications 5% (Microsoft Digital Defense Report 2026, global).
- Over half (52.2%) of the intrusions that began with a valid account went on to harvest more credentials, and 18.4% involved an active password spray; ClickFix attacks fell from 47% of observed initial access in the previous year to 12.8%, then grew roughly 23-fold between December 2025 and May 2026 (Microsoft Digital Defense Report 2026).
- Business email compromise and funds transfer fraud together accounted for 58% of all Coalition cyber insurance claims in 2025, and 71% of funds transfer fraud claims were a direct result of social engineering (Coalition 2026 Cyber Claims Report, policyholders in the UK, US, Canada, Australia and Germany).
- Email was the entry point in 52% of At-Bay’s 2025 claims and 82% of its financial fraud claims, but no At-Bay ransomware claim in 2025 started with email (At-Bay InsurSec Report 2026, US-weighted).
Have a think about the gap between 93% and 16%. Both are true. If you run a UK business, almost every cyber crime you experience will be a phishing email. If you are investigating a breach that got as far as data theft, there is a better than even chance it started somewhere else. Both numbers belong in a board paper; only one belongs in the training budget.
Suggested Read: Cyber Security Statistics
3. Who falls for phishing? UK adults and employees
There is less good data on this than you would expect. The ONS has published one dedicated UK study, in 2022, and nothing since; the newer figures come from Ofcom’s scam research, the Crime Survey and the phishing simulation data in the DBIR.
UK adults
- Half of UK mobile users said they had received a suspicious text or iMessage between November 2024 and February 2025, around 100 million suspicious messages were reported to the 7726 service in the year to April 2025, and mobile providers block an estimated 600 million scam messages a year (Ofcom, Combatting mobile messaging scams, October 2025).
- The Crime Survey for England and Wales estimated 4.5 million fraud incidents in the year to March 2026, with 7.8% of adults a victim, and 798,000 computer misuse incidents (ONS, Crime in England and Wales: year ending March 2026, July 2026).
- Where there was contact between fraudster and victim, the first contact was by telephone in 39% of cases, online including social media in 32%, email in 13% and text message in 4% (ONS, Nature of fraud and computer misuse, year ending March 2025, published March 2026).
- The only official UK study of phishing by age found that half of adults had received a phishing message in the previous month, that 35 to 44 year olds (60%) and 25 to 34 year olds (58%) were most likely to receive one, that 3% of recipients replied or clicked (over 700,000 people) and that 35 to 44 year olds were most likely to click at 4.8%. Delivery companies (54%), banks (32%) and government services (25%) were the most impersonated senders (ONS, Phishing attacks: who is most at risk, September 2022, fieldwork October 2021 to March 2022; the only dataset of its kind).
Employees and phishing simulations
- The median click rate in email phishing simulation campaigns was 1.4%. For phone-centric simulations (voice and text) the median was closer to 2%, a 40% higher success rate, although the sample of non-email campaigns was small (Verizon DBIR 2026, 8,395 email campaigns and 35 non-email campaigns, global).
- Measured per attempt, bulk phishing email gets 1% to 5% of recipients to engage or click and targeted email 30% to 40%, while a voice phishing call keeps 48% of targets on the line for more than 20 seconds and 30% for more than a minute. Across the vishing attacks Microsoft studied, 93% of attackers succeeded at least once in holding a target past the 20-second mark at which a social engineering script can begin (Microsoft Digital Defense Report 2026, Microsoft and academic telemetry). The voice and helpdesk side of that is on our social engineering statistics page.
- 22% of UK businesses and 13% of charities test staff with mock phishing exercises, and 19% of businesses and 17% of charities ran staff training or awareness activities in the year. 58% of businesses and 94% of large businesses have an agreed process for staff to follow when they identify a fraudulent email (CSBS 2025/26).
- In the last UK survey Proofpoint published, 66% of UK organisations had at least one successful phishing attack in 2023, down from 91% the year before, and 70% of UK working adults admitted to taking a risky action (Proofpoint State of the Phish 2024, 2023 data; no later edition has been published).
In our phishing simulation and social engineering assessments we see the same pattern the DBIR describes: the first campaign against an untrained workforce lands well above the 1.4% median, the click rate falls quickly once people know simulations are running, and the thing that does not fall is the time between the first click and the first report. A low click rate with no reports is a worse position than a higher click rate with fast reporting, because the second one gives the IT team a chance to act before the credentials are used.
This is why having a human risk management solution in your organisation allows stakeholders to tackle the phishing problems because it allows you to tailor training programs based on your sector, departments, , run simulations and more importantly assess the improvements.
Suggested Read: Social Engineering Statistics
4. Phishing statistics by industry
Sector data comes in two kinds: which sectors report the most phishing breaches, and which sectors’ brands are impersonated. The ICO dataset answers the first for the UK; the APWG and Kaspersky answer the second globally.
UK sectors reporting phishing breaches to the ICO, 2025
| Sector | Phishing breach reports 2025 | 2024 |
|---|---|---|
| Retail and manufacture | 322 | 287 |
| Finance, insurance and credit | 176 | 179 |
| Charitable and voluntary | 158 | 121 |
| Education and childcare | 156 | 141 |
| Legal | 153 | 174 |
| Land or property services | 129 | 92 |
| Transport and leisure | 112 | 92 |
| Health | 98 | 65 |
| Online technology and telecoms | 49 | 30 |
| General business | 46 | 50 |
Source: our count of unique incident references in the ICO data security incident trends dataset. Retail and manufacture also reported the most cyber breaches of any kind (805 in 2025).
- Phishing was the initial access vector in 22% of education breaches, 20% of finance and insurance breaches, 20% of public administration breaches, 14% of healthcare breaches and 13% of manufacturing breaches (Verizon DBIR 2026, global).
- Manufacturing and government were the primary targets for email phishing in 2025; phishing hits against the services sector rose 65.5% year on year and against government rose 50% (Zscaler ThreatLabz 2026 Phishing and Initial Access Report, telemetry January to December 2025, global).
- SaaS and webmail was the most-impersonated sector in the second quarter of 2026 at 29.1% of phishing attacks, followed by payment (13.2%), financial institutions (11.4%), logistics and shipping (9.6%), social media (8.5%) and cryptocurrency (7.2%). Telecom was 33% in the first quarter and fell to 4.2% (APWG Q2 2026, global).
- Phishing pages impersonating web services were 27.42% of Kaspersky’s 2025 detections, global internet portals 15.89%, online stores 11.27%, gaming platforms 7.58%, banks 6.06%, payment systems 5.93%, messengers 5.70% and delivery services 5.06% (Kaspersky Spam and Phishing in 2025, February 2026, global).
Suggested Read: Healthcare Cyber Attack Statistics
5. Phishing statistics by country
- The UK was the fourth largest source of complaints to the FBI’s IC3 outside the US in 2025, with 4,106 complainants, behind Canada (7,479), India (5,879) and Japan (5,764) (IC3 2025, US-collected).
- Phishing was the initial access vector in 28% of breaches in Europe, the Middle East and Africa, against 20% in Latin America, 15% in Asia-Pacific and 12% in North America; EMEA also had the highest share of state-affiliated actors (23% against 14% overall) (Verizon DBIR 2026).
- Peru had the highest share of users who encountered phishing in 2025 at 17.46%, followed by Bangladesh (16.98%), Malawi (16.65%) and Tunisia (16.19%); the UK does not appear in the top ten (Kaspersky Spam and Phishing in 2025, share of Kaspersky users per country).
6. How phishing is delivered: email, SMS, QR codes, social media and AI
Email is still the main channel, but the growth is everywhere else. Every report in this section that measures more than one channel shows text, voice, QR and social media growing faster than email.
- Microsoft screens about 5.2 billion emails a day for malware and phishing and detected about 8.3 billion email-based phishing threats in the first quarter of 2026 alone, 78% of them link-based (Microsoft Digital Defense Report 2026; Microsoft Threat Intelligence, Email threat landscape Q1 2026).
- Malicious attachments are now a vehicle for credential theft rather than malware: in every month between July 2025 and June 2026, between 89% and 96% of malicious attachments sent the user to a phishing page or a fake sign-in rather than delivering malware. HTML was the most common malicious attachment type in ten of the twelve months, PDF volume rose 38% in February 2026 and a further 50% in March, and SVG payloads fell from 23% of malicious attachments to 7% over the year (Microsoft Digital Defense Report 2026, Defender for Office 365 telemetry).
- Adversary-in-the-middle (AiTM) phishing, where a reverse proxy sits between the user and the real sign-in page and steals the session cookie as well as the password and MFA code, is now 44.6% of identified phishing techniques (AiTM links 45% and AiTM attachments 7%), against 33.6% for standard URL phishing and 12.9% for traditional attachments; 87.7% of phishing intrusions involved credential or session harvesting and 6.3% were business contact impersonation (Microsoft Digital Defense Report 2026, Defender Experts data).
- The phishing-as-a-service platform Tycoon2FA, which sells AiTM infrastructure on Telegram, was linked to more than 15.1 million malicious emails a month in the second half of 2025, reached over 500,000 organisations a month and accounted for up to 9% of all malicious messages Microsoft detected. After Microsoft, Europol and partners disrupted its hosting in March 2026, its activity fell 95% from the November 2025 peak and its share of malicious email dropped from roughly 11% to 1.5% by April 2026 (Microsoft Digital Defense Report 2026).
- Device code phishing, which sends the target to Microsoft’s real device sign-in page and harvests the OAuth tokens that result, has moved from a niche technique to a preferred credential theft method for both state and criminal actors, with lures such as DocuSign requests, voicemail alerts and construction bid documents that were often personalised and potentially AI-generated (Microsoft Digital Defense Report 2026).
- Overall phishing volume fell 20% year on year in Zscaler’s 2025 telemetry, the second consecutive annual fall, as attackers traded mass volume for targeted campaigns; 95.2% of phishing attempts were hidden in encrypted traffic (Zscaler ThreatLabz 2026).
- The APWG recorded 3.8 million phishing attacks (unique phishing sites) in 2025, up slightly from 3.76 million in 2024. Quarterly totals ran 853,244 in Q4 2025, 971,181 in Q1 2026 and 1,069,681 in Q2 2026; the 425,808 attacks in June 2026 were the most in a month since April 2023 (APWG Q4 2025, Q1 2026 and Q2 2026).
SMS, voice and messaging apps
- Smishing (SMS phishing) rose 40% and vishing (voice phishing) rose 20% between the first and second quarters of 2026; telephone-based fraud rose 15% the quarter before, and SMS fraud detections had been growing 30% to 40% quarter on quarter through 2025 (APWG Q4 2025, Q1 2026 and Q2 2026, Crane Authentication data).
- Telecommunications was the channel behind 17% of UK authorised push payment fraud cases and 28% of losses in 2025; online sources enabled 66% of cases and 32% of losses; email enabled 1% of cases but 7% of losses (UK Finance Annual Fraud Report 2026, from closed cases on the Best Practice Standards platform).
- The only published breakdown of phishing links by messaging app remains Kaspersky’s December 2020 to May 2021 data: 89.6% of the 91,242 malicious links its users encountered in messengers were on WhatsApp, 5.6% on Telegram and 4.7% on Viber (Kaspersky, July 2021; older than our usual cut-off, kept because nothing newer exists).
QR codes and CAPTCHA-gated pages
- Microsoft Defender for Office 365 detected more than 145 million QR code phishing attacks between July 2025 and June 2026. Volume fell through the second half of 2025 to a low in January 2026, rose from 7.6 million detections in January to 18.7 million in March (an all-time high) and then more than halved by June; PDF attachments carried 79% of QR attacks by April 2026 (Microsoft Digital Defense Report 2026; Microsoft Threat Intelligence, Q1 2026).
- More than 100 million phishing attacks in the same twelve months put a CAPTCHA page between the victim and the credential harvesting site so that automated scanners could not see it. Delivery rotated from embedded URLs (58% in August 2025) to SVG files (47% in November) to PDFs (nearly two thirds by April 2026). Tycoon2FA alone grew from 9% of CAPTCHA-gated phishing in July 2025 to 76% in December, then fell to 12% by June 2026 after the disruption (Microsoft Digital Defense Report 2026).
Social media and adverts
- Threats on Meta Ads rose 571% between the first and second quarters of 2026, with LinkedIn up 106% and Facebook up 88%; impersonation (32.7%) and scams (22.8%) were the main threat types on social platforms (APWG Q2 2026, ZeroFox data).
AI-generated phishing and attacks on AI agents
The 2026 data is the first year in which the primary reports describe AI on both sides of a phishing attack: generating the lure, and being the thing the lure is aimed at.
- Microsoft’s assessment is that generative AI now lets “every phishing attack become targeted and personalized, allowing for spear phishing at scale”, with context-aware lures built from details about a person or company and adaptive back-ends that change their signatures to evade sandboxing; it reports that in most real-world operations the end-to-end intrusion still retains human direction, with AI used for reconnaissance, data triage, lure writing and, increasingly, malware development (Microsoft Digital Defense Report 2026).
- In 2025 an AI-augmented ClickFix campaign spread through TikTok, using faceless tutorial videos with synthetic narration that ended in a malicious command fetching the Vidar or StealC infostealer; near-identical scenes signalled automated lure production, some videos topped around 500,000 views, and AI drove the cost of each lure to near zero (Microsoft Digital Defense Report 2026).
- A malicious browser extension posing as an AI assistant, with over 600,000 installs, harvested ChatGPT and DeepSeek conversation histories from almost 10,000 organisations before it was mitigated in December 2025; Microsoft notes that LLM conversation history now routinely contains source code, customer data and credentials (Microsoft Digital Defense Report 2026).
- 88% of enterprises are already experimenting with AI agents and 82% of leaders plan broader rollouts within 12 to 18 months. Of the prompts Microsoft observed being aimed at generative AI agents between February and May 2026, 45% were attempts at malicious or policy-violating use, which includes drafting phishing emails and fraudulent invoices, 17% sought to exfiltrate sensitive data, 14% to leak the system prompt and 12% to hijack the agent’s goal or its downstream tools (Microsoft Digital Defense Report 2026).
- In telemetry from Azure AI workloads, four techniques made up roughly 90% of attack activity: malicious link injection routed through model and tool outputs (52%), jailbreak and safety bypass attempts (16%), tool and agent abuse (12%) and identity and credential abuse (10%), with prompt injection at 8%. Phishing links delivered through an AI agent’s own output are now the largest single category of attack on AI workloads (Microsoft Digital Defense Report 2026).
- Zscaler identified 413,524 AI-generated site instances in 2025, nearly 10% flagged as explicitly malicious, built with tools such as Manus, Blackbox and Lovable (Zscaler ThreatLabz 2026).
- ChatGPT entered the ten most impersonated brands for the first time in the second quarter of 2026, with fake subscription failure emails leading to card detail harvesting pages (Check Point Research, Q2 2026).
7. Brand impersonation and the lures that work
- Microsoft was the most impersonated brand in the second quarter of 2026, appearing in 23% of brand phishing attempts, nearly double the next brand. Microsoft, LinkedIn, Google, Apple and Amazon together accounted for more than half of all brand phishing, and technology was the most impersonated industry, followed by social networks and banking (Check Point Research Brand Phishing Report Q2 2026, July 2026, global).
- Nearly 85% of reported phishing emails between April and June 2026 carried an impersonation signal. 32% of attacks used images or logos to mimic a brand, more than a third used template lures that copy familiar brand communications without naming the brand, and 44% of the brands targeted were lesser-known or location-specific ones that fall outside globally tuned detection (Microsoft Digital Defense Report 2026).
- The shift is from brand mimicry to context mimicry: 80% of impersonation attacks posed as automated notifications and 61% used financial fraud themes; around 25% mimicked the target’s own organisation or someone inside it, and HR, payroll and benefits scams drove 77% of those. One in four impersonation emails pushed the victim to a phone call, moving the attack outside URL and attachment inspection (Microsoft Digital Defense Report 2026).
- Gift cards were the cash-out method in 55% of BEC attempts in the second quarter of 2026, wire transfer 17%, payroll diversion 10%, Interac 9% and cryptocurrency 6% (APWG Q2 2026, Fortra data).
We have dropped the subject line and keyword statistics (“urgent”, “invoice”, empty subject lines) that used to appear here. They came from 2021 vendor telemetry and no publisher has released a comparable 2025 or 2026 breakdown with a stated method.

8. What phishing costs: business email compromise and payment diversion fraud
Phishing on its own rarely has a price tag. The cost arrives as business email compromise, payment diversion fraud and account takeover, which is where the UK’s fraud reporting bodies and the insurers’ claims data pick it up.
- Payment diversion fraud (mandate fraud, the UK label for BEC) was reported 3,657 times in 2025/26 with £101 million in losses, down 24% on the previous year; invoice fraud was the largest sub-type at 813 reports (Report Fraud Annual Assessment FY2025-26).
- Business email compromise was 17% of the cyber incidents Pinsent Masons handled in 2025. In 44% of those the attacker had synchronised the mailbox, and in 33% invoice fraud was carried out (Pinsent Masons Cyber Annual Report 2026).
- Microsoft now separates the two things people call BEC: credential phishing and account takeover on one side, and “business contact impersonation” (BCI), the social engineering conversation that poses as an executive, employee, supplier or partner, on the other. It detected more than 46 million BCI attacks in the twelve months to June 2026, with monthly volume spiking 121% in April 2026. The first message rarely asks for anything: the share of initial BCI emails containing an explicit financial or document request fell from 17% in October 2025 to 3% by June 2026, and 51% of payroll diversion attempts land on a Monday or Tuesday, timed for when HR and payroll staff are clearing the previous week’s requests (Microsoft Digital Defense Report 2026, global).
- 3% of UK businesses (around 43,000) and 1% of charities were victims of fraud as a result of a cyber breach, around 130,000 cyber-facilitated fraud events in the year. The median cost was £110 across all victims and £500 among those with a non-zero cost; the top 10% of costs started at £12,000 (CSBS 2025/26).
- Authorised push payment fraud losses in the UK rose 19% to £576.4 million in 2025 across 248,070 cases, £75.6 million of it from businesses. 88% of in-scope APP losses were reimbursed in the first year of the Payment Systems Regulator’s mandatory reimbursement rules, which took effect on 7 October 2024 (UK Finance Annual Fraud Report 2026).
- Business email compromise claims averaged about £20,000 and funds transfer fraud about £106,000 on Coalition’s book in 2025, and 52% of funds transfer fraud claims began as a business email compromise, with an average loss of £83,000 (Coalition 2026 Cyber Claims Report, sterling converted at 1.35).
- The average amount requested in a wire transfer BEC attack was $61,732 in the second quarter of 2026, up 45% on the $42,663 of the first quarter, and the number of wire transfer BEC attacks rose 88% in the quarter (APWG Q2 2026, Fortra data, global).
- Business email compromise cost US victims $3.05 billion across 24,768 complaints in 2025, up from $2.77 billion in 2024, and phishing and spoofing was the most reported crime type with 191,561 complaints and $215.8 million in direct losses (IC3 2025, US).
Suggested Read: Cyber Insurance Statistics
9. Recent UK phishing incidents, 2025 to 2026
Two incidents from the last eighteen months show what the figures above look like on the ground. We have left out the April 2025 retail attacks on Marks and Spencer, the Co-op and Harrods on purpose: those started with helpdesk impersonation over the phone, not phishing, and belong on the social engineering page.
HM Revenue and Customs, June 2025. HMRC told the Treasury Committee that criminals had used phishing to obtain the personal details of around 100,000 taxpayers and then used them to access PAYE accounts and claim repayments, costing around £47 million. The Committee called HMRC’s failure to report the breach to Parliament sooner “unacceptable” (Treasury Committee, 10 June 2025).
South Staffordshire Water, fined May 2026. The ICO fined South Staffordshire Plc and South Staffordshire Water Plc £963,900 for an attack that began when an employee opened an attachment in a phishing email. The malware went undetected for 20 months, the attacker gained domain administrator privileges in May 2022, and the personal data of 633,887 people was published on the dark web in August 2022. Only 5% of the IT environment was monitored (ICO, 11 May 2026).
Suggested Read: Small Business Cyber Attack Statistics
Frequently asked questions
How common is phishing in the UK?
38% of UK businesses and 25% of charities experienced phishing in the last 12 months, and it accounted for 93% of the cyber crimes businesses reported. The NCSC received over 10.9 million suspicious email reports in the year to August 2025 (CSBS 2025/26; NCSC Annual Review 2025).
What percentage of cyber attacks are phishing?
It depends on the measure. Phishing was 93% of cyber crimes experienced by UK businesses, 48% of cyber breaches reported to the ICO in 2025, the root cause of just under half of UK ransomware attacks (malicious email 25% plus phishing 22%), and the initial access vector in 16% of breaches worldwide and 28% in EMEA (CSBS 2025/26; ICO; Sophos UK 2026; Verizon DBIR 2026).
What percentage of phishing attacks are successful?
The median click rate in email phishing simulations is 1.4%, rising to around 2% for text and voice. Among UK adults who received a phishing message, 3% replied or clicked. At organisation level, 66% of UK organisations reported at least one successful phishing attack in the last UK survey Proofpoint published (Verizon DBIR 2026; ONS 2022; Proofpoint 2024).
How many people fall for phishing scams?
The ONS estimated that over 700,000 adults in England and Wales replied to or clicked on a phishing message in a month in 2021/22, the only official UK estimate. The Crime Survey recorded 4.5 million fraud incidents in the year to March 2026, with 7.8% of adults a victim (ONS).
Who is most vulnerable to phishing?
In the UK, adults aged 35 to 44 were both the most likely to receive phishing messages (60%) and the most likely to click (4.8%), not the oldest age groups. In the US, people aged 60 and over reported the most complaints and the largest losses (ONS 2022; IC3 2025).
How much does phishing cost UK businesses?
Payment diversion fraud cost UK victims £101 million across 3,657 reports in 2025/26. The median cost of cyber-facilitated fraud to a UK business was £110 including zero-cost cases, and the top 10% of cases started at £12,000. Business email compromise claims averaged about £20,000 and funds transfer fraud about £106,000 on Coalition’s book (Report Fraud; CSBS 2025/26; Coalition 2026).

About this data
This page draws on reports published between October 2025 and September 2026, with the DSIT Cyber Security Breaches Survey 2025/26 (fieldwork autumn 2025, published 30 April 2026) as the UK spine. UK figures come from DSIT, the NCSC Annual Review 2025, the ICO, Report Fraud and the City of London Police, UK Finance, Ofcom, the ONS, Pinsent Masons and Sophos’s UK survey. Global and US figures come from the APWG quarterly reports (Q4 2025 to Q2 2026), Verizon’s 2026 DBIR, the Microsoft Digital Defense Report 2026 (reporting period July 2025 to June 2026, published October 2026) and Microsoft’s Q1 2026 email threat report, the FBI’s 2025 Internet Crime Report, Zscaler, Check Point Research, Kaspersky, Coalition and At-Bay. Where a report covers several countries we have said so in the line.
ICO figures are our own count of unique incident references in the ICO’s published data security incident trends dataset (Q1 2019 to Q4 2025), by year, quarter, incident type and sector. Coalition’s sterling figures are its own conversions at 1.35 dollars to the pound. Two figures are older than our usual cut-off and are labelled as such: the ONS 2022 study of UK adults, because the ONS has not repeated it, and Kaspersky’s 2021 messenger breakdown, because no newer breakdown exists.
Older figures from 2016 to 2022 that appeared in previous versions of this page have been removed, including the 2022 APWG tables, the subject line statistics and the Crelan and FACC case studies. We refresh this page after each Cyber Security Breaches Survey (April), each NCSC Annual Review (October) and each APWG quarterly report.
If you cite a figure from this page, please link to the original source as well as to us; the references are below.
References
- DSIT, Cyber Security Breaches Survey 2025/26 (30 April 2026)
- NCSC Annual Review 2025, Active Cyber Defence chapter (14 October 2025)
- ICO, Data security incident trends dataset (Q1 2019 to Q4 2025)
- City of London Police, Report Fraud Annual Assessment FY2025-26: Cyber Crime and Fraud (September 2026)
- Ofcom, New rules to protect people and businesses against mobile messaging scams (29 October 2025)
- UK Finance, Annual Fraud Report 2026 (15 June 2026)
- UK Finance, press release: Fraud remains a national security threat (15 June 2026)
- ONS, Crime in England and Wales: year ending March 2026 (23 July 2026)
- ONS, Nature of fraud and computer misuse in England and Wales: year ending March 2025 (26 March 2026)
- ONS, Phishing attacks: who is most at risk? (26 September 2022)
- Sophos, State of Ransomware in the UK 2026 (July 2026)
- Pinsent Masons, Cyber Annual Report 2026
- Verizon, 2026 Data Breach Investigations Report
- Verizon, 2026 DBIR Executive Summary
- Coalition, 2026 Cyber Claims Report
- At-Bay, 2026 InsurSec Report (April 2026)
- FBI IC3, 2025 Internet Crime Report (April 2026)
- Proofpoint, 2024 State of the Phish, UK findings (27 February 2024)
- Zscaler, ThreatLabz 2026 Phishing and Initial Access Report, press release (10 June 2026)
- APWG, Phishing Activity Trends Report, 4th Quarter 2025 (18 February 2026)
- APWG, Phishing Activity Trends Report, 1st Quarter 2026 (21 May 2026)
- APWG, Phishing Activity Trends Report, 2nd Quarter 2026 (28 August 2026)
- Kaspersky (Securelist), Spam and phishing in 2025 (11 February 2026)
- Kaspersky, Phishing in messenger apps: what’s new? (12 July 2021)
- Microsoft, Digital Defense Report 2026 (October 2026)
- Microsoft, Digital Defense Report 2026 full report (PDF)
- Microsoft Threat Intelligence, Email threat landscape Q1 2026: trends and insights (30 April 2026)
- Check Point Research, Which brands are impersonated most? Q2 2026 Brand Phishing Report (23 July 2026)
- Treasury Committee, HMRC warned by Committee for handling of phishing attack (10 June 2025)
- ICO, Fine of nearly £1m issued against South Staffordshire Plc and South Staffordshire Water Plc (11 May 2026)