Most of the cyber incidents we get called into in the UK did not start with a clever exploit. They started with a person: a finance clerk who paid a changed invoice, a helpdesk agent who reset a password for a caller who sounded right, an employee who approved one more MFA prompt to make the notifications stop. Social engineering is the name for all of that, and in 2025 it was the entry route for the most expensive cyber attacks the UK has seen.
In this article we have pulled together the latest statistics on social engineering from the organisations that actually hold the data: the government’s Cyber Security Breaches Survey, the NCSC, UK Finance, Ofcom, City of London Police, the ONS, and the insurers, lawyers and incident responders who publish their own claims and caseload figures. UK data comes first in every section. Where a figure is global or US-only we say so in the line, because a lot of what circulates online is American and gets quoted as if it applied here.
Phishing has its own page on this site, so here we only cross-reference it. This page covers the rest of the human element: impersonation, voice and helpdesk attacks, text message scams, business email compromise and funds transfer fraud, pretexting, MFA bypass, and AI-enabled deepfake fraud, plus what the 2025 attacks on M&S, Co-op and Jaguar Land Rover tell us.
Key social engineering statistics for 2026 at a glance
- 12% of UK businesses and 7% of charities identified people impersonating their organisation or staff in emails or online in the last 12 months, rising to 38% of medium and 47% of large businesses (Cyber Security Breaches Survey 2025/26, DSIT, April 2026).
- Only 19% of UK businesses ran any staff cyber security training or awareness activity in the last year, and 22% tested staff with mock phishing (CSBS 2025/26).
- UK police and bank impersonation scams cost victims £55.5 million across 6,016 cases in 2025; invoice and mandate scams £41.3 million; CEO fraud £5.6 million at an average of just over £28,000 per case (UK Finance Annual Fraud Report 2026).
- Courier fraud, where callers pose as police or bank staff, drew 1,891 reports and over £21 million in losses in 2025, an average of £15,311 per victim (City of London Police, June 2026).
- 42% of UK phone users received a suspicious call and 50% of mobile users a suspicious text in the three months to February 2025; the text figure was 75% in 2021 (Ofcom, 2025 research).
- The NCSC handled 429 incidents in the year to August 2025, 204 of them nationally significant, more than double the 89 of the year before (NCSC Annual Review 2025).
- The combined cost of the April 2025 M&S and Co-op attacks, both of which began with social engineering, is estimated at £270 million to £440 million (Cyber Monitoring Centre, June 2025).
- The human element was present in 62% of breaches worldwide, and the Social Engineering pattern accounted for 16% of all breaches (Verizon DBIR 2026, global).
- Voice phishing was the initial intrusion vector in 11% of intrusions investigated in 2025, the second most common route and ahead of email phishing at 6% (Mandiant M-Trends 2026, global).
- 71% of funds transfer fraud claims were a direct result of social engineering, and business email compromise plus funds transfer fraud made up 58% of all cyber claims (Coalition 2026 Cyber Claims Report, global policyholders).
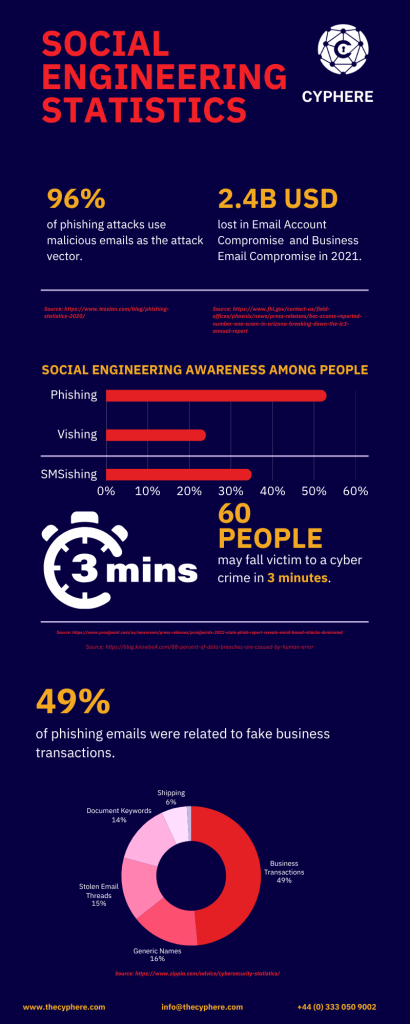
Social engineering statistics – Infographic
1. How common is social engineering in the UK?
The Cyber Security Breaches Survey is the only official measure of how many UK organisations are hit. The 2025/26 edition surveyed 2,112 businesses and 1,085 charities between August and December 2025 and was published on 30 April 2026. It records impersonation as a distinct category from phishing, which is the figure this page follows.
- 12% of all UK businesses identified people impersonating their organisation or staff in emails or online in the last 12 months, down from 17% in 2023/24, with significant falls across all business sizes (CSBS 2025/26).
- 7% of charities identified impersonation, down from 11% in 2024/25 and 12% in 2023/24 (CSBS 2025/26).
- Among organisations that identified any breach or attack, 28% of businesses and 26% of charities had an impersonation incident, second only to phishing at 88% and 87% (CSBS 2025/26).
- Impersonation was the single most disruptive incident for 13% of businesses that had a breach, down from 18% in 2024/25, and for 16% of charities, down from 24% in 2023/24 (CSBS 2025/26).
- For context, phishing remained the most common breach type at 38% of businesses and 25% of charities; the full phishing data is on our phishing statistics page (CSBS 2025/26).
- 19% of businesses and 14% of charities were victims of at least one cyber crime in the last year, roughly 267,000 businesses and 28,000 charities, and businesses experienced around 5.19 million cyber crimes in total (CSBS 2025/26).
- 3% of businesses and 1% of charities were victims of fraud that resulted from a cyber breach, about 43,000 businesses and 130,000 fraud events; the median cost was £110 including zero-cost cases and £500 excluding them, with the top 10% of cases costing £12,000 or more (CSBS 2025/26).
- The NCSC received 1,727 incident tips and handled 429 incidents between September 2024 and August 2025; 204 (48%) were nationally significant and 18 were highly significant, a 50% rise in the top category for the third consecutive year (NCSC Annual Review 2025).
- The NCSC’s Suspicious Email Reporting Service received over 10.9 million reports in the year to August 2025, taking the total since April 2020 past 45 million, and the NCSC has removed 412,000 malicious URLs since 2020 (NCSC Annual Review 2025).
- Across the general population, the Crime Survey for England and Wales estimates 4.5 million fraud incidents against 3.8 million victims in the year to March 2026; 7.8% of people aged 16 and over were defrauded (ONS, July 2026).
The table below sets out where the human element shows up by business size. The size gradient is the point: the larger the organisation, the more staff there are to impersonate and the more often somebody is targeted, but the training figures do not scale with it.
| Measure (last 12 months) | All businesses | Medium (50 to 249) | Large (250+) |
|---|---|---|---|
| Identified impersonation of organisation or staff | 12% | 38% | 47% |
| Identified phishing | 38% | 60% | 63% |
| Ran staff training or awareness activity | 19% | 54% | 84% |
| Experienced a cyber crime | 19% | 41% | 48% |
Source: Cyber Security Breaches Survey 2025/26, DSIT.
Suggested Read: Phishing Statistics
2. The human element in breaches: global and UK data
The UK survey counts organisations; the incident response and breach datasets count what actually happened once an attacker got in. Both point the same way.
- The human element was present in 62% of breaches analysed, up from 60% the year before, and the Social Engineering pattern was the third most common breach pattern at 16% of all breaches (Verizon DBIR 2026, 22,000+ breaches, global).
- The Social Engineering pattern covered 5,302 incidents, 3,814 of them with confirmed data disclosure (DBIR 2026).
- By initial access vector across all breaches, vulnerability exploitation reached 31%, phishing 16%, credential abuse 13% and pretexting 6%; pretexting was added as a tracked vector this year because of the number of high-profile ransomware breaches that began with it (DBIR 2026).
- 41% of Social Engineering breaches involved vectors other than email, and about a quarter of social action vectors came through social media or phones (DBIR 2026).
- Social engineering tactics, with phishing including vishing, malspam and malvertising, accounted for about 60% of observed initial intrusions in Europe, against 21.3% for vulnerability exploitation, across 4,875 incidents from July 2024 to June 2025 (ENISA, October 2025, EU-weighted).
- Voice phishing was the initial infection vector in 11% of intrusions investigated in 2025, second only to exploits at 32%; email phishing fell to 6% as automated email controls improved (Mandiant M-Trends 2026, global).
- More than 97% of identity attacks are password attacks, and identity-based attacks rose 32% in the first half of 2025; phishing-resistant MFA blocks over 99% of them (Microsoft Digital Defense Report 2025, July 2024 to June 2025, global).
- Phishing and other email-based social engineering was the initial entry vector in 34% of ransomware incidents, and in 40% of cases employees did not suspect the attack because it appeared authentic (Proofpoint 2026 AI-Era Ransomware Report, 953 respondents in 12 countries including the UK).
- 22% of UK organisations reported AI-generated attacks in the past year, and the UK average breach cost was £3.13 million, down from £3.29 million (IBM Cost of a Data Breach Report 2026, UK sample).
- Business email compromise accounted for 17% of the UK incidents Pinsent Masons’ cyber team handled in 2025, down from 26% in 2024; in 44% of those cases the attacker synchronised the mailbox and in 33% invoice fraud followed (Pinsent Masons Cyber Annual Report 2026).
- Our count of the ICO’s data security incident dataset shows phishing was the reported cause of 1,526 of the 3,153 cyber breaches notified to the ICO in 2025 (48%), up from 1,380 of 3,116 in 2024 (44%) and 924 of 3,319 in 2023 (28%), while ransomware reports fell from 1,253 to 617 over the same period. Phishing is covered on the phishing page; the trend matters here because it shows the entry point shifting from malware to people.
Our view is that the 62% and 16% figures answer two different questions and get confused. The human element figure counts every breach where a person made an error, used a weak password or was manipulated. The 16% is the narrower set where social engineering was the attack pattern itself. Both are right; quote the one that matches the claim you are making.
3. Vishing, helpdesk impersonation and MFA bypass
Voice attacks are the part of social engineering that has changed most since 2023. The consumer data from Ofcom and UK Finance shows the volume; the incident data shows why attackers moved to the phone: it works on helpdesks.
UK consumer data
- 42% of UK phone users received a suspicious call on a landline or mobile in the three months to February 2025, and most of them received such calls at least once a month (Ofcom, Experiences of suspicious calls, texts and app messages, 2025).
- 26% of people said they were likely to answer a call from an unrecognised UK mobile number, 19% a withheld number and 9% an unrecognised international number (Ofcom, 2025).
- Police and bank impersonation scams, usually a call or text claiming fraud on the account and a transfer to a “safe account”, cost £55.5 million across 6,016 cases in 2025, down 18% and 23% respectively and the lowest totals ever recorded; 80% of losses were returned to victims (UK Finance Annual Fraud Report 2026).
- Other impersonation scams (utilities, telecoms providers, government departments, including remote-access “fix your computer” calls) cost £36.9 million across 18,435 cases in 2025 (UK Finance 2026).
- Telecommunications were the channel in 17% of authorised push payment fraud cases but 28% of losses in 2025, because phone-based impersonation produces higher-value cases than online scams, which were 66% of cases and 32% of losses (UK Finance 2026).
- Courier fraud, where a caller posing as a police officer or bank employee sends a courier to collect cash, cards or jewellery, drew 1,891 reports in 2025, up nearly 10% on 1,721 in 2024, with losses above £21 million and an average loss of £15,311 per victim; victims aged 76 to 96 accounted for around 62% of reports (City of London Police, June 2026).
- Where fraud victims had direct contact with the offender, 38% of cases started by telephone and 12% by text message in the year to March 2024; in 91% of all cases there was no direct contact (ONS Crime Survey, cited by Ofcom, 2025).
Helpdesk impersonation and MFA bypass in organisations
- In phishing simulations, the median click rate for phone-centric vectors (voice and text) was close to 2%, 40% higher than the 1.4% median for email campaigns; the DBIR notes that attackers have been impersonating help desk agents, or users needing a password reset, “with moderate levels of success” (DBIR 2026).
- Pretexting became a more common initial access vector for ransomware and extortion, reaching 6% of all breaches (DBIR 2026).
- The joint advisory on Scattered Spider, updated in July 2025 by CISA, the FBI and the UK, Canadian and Australian cyber agencies, lists the group’s techniques as posing as IT or helpdesk staff by phone or text, persuading helpdesks to reset passwords and MFA tokens, harvesting one-time codes, push bombing employees with MFA prompts until one is approved, and SIM swapping (CISA AA23-320A, 2025 update).
- The NCSC’s first public advice during the April 2025 retail attacks was to “review helpdesk password reset processes”, in particular how the helpdesk verifies staff before resetting passwords on accounts with elevated privileges (NCSC, 4 May 2025).
- The NCSC Annual Review 2025 describes “impersonating a user on helpdesk calls to reset an identity’s access credentials” as one of the ways identity systems are now broken (NCSC, October 2025).
- Among the “Scattered Spider” techniques, none require malware; the DBIR describes a common 2025 pattern in which attackers flood a user with spam, then contact them on Microsoft Teams posing as the helpdesk and ask for remote access to “fix” it (DBIR 2026).
There is no published UK figure for how often MFA fatigue or helpdesk resets succeed, and we would be wary of anyone quoting one. What we can say is that in our own social engineering assessments the helpdesk password-reset call is the test most organisations fail: the agent asks for an employee number and a date of birth, both of which are in the last data breach, and resets the password within the call. Verification that depends on information rather than on a callback to a known number or a manager’s approval is the gap the retail attackers walked through.
Suggested Read: Social Engineering
4. Smishing and mobile social engineering statistics
- 50% of UK mobile users received a suspicious SMS, RCS or iMessage in the three months to February 2025, down from 75% in 2021, a fall Ofcom puts at roughly 10% a year as network filtering improved (Ofcom, 2025 research, cited in Ofcom’s October 2025 consultation).
- Ofcom estimates at least 100 million suspicious messages still reach UK mobile users each year, after operators blocked at least 600 million; blocking averaged just over 30 million a month between May 2024 and March 2025 and passed 50 million in February and March 2025 (Ofcom, October 2025).
- Reports to the 7726 text-reporting service exceeded 100 million in the year to March 2025 (Ofcom, October 2025).
- Ofcom’s own estimate of losses from messaging scams is around £65 million a year, of which about £25 million is authorised push payment fraud that started with a text (Ofcom, October 2025).
- Large organisations saw a median of 48 SMS phishing campaigns a year reach managed mobile devices, and smaller organisations 12; those were only visible because the devices were managed (DBIR 2026, global).
- Mobile social engineering, meaning fake texts and voice calls, had a success rate 40% higher than email phishing in simulation data (Verizon, May 2026).
- The share of UK adults who follow a scam message’s instructions has not been measured since Ofcom’s 2021 survey, when it was 2%, roughly one million people in three months; treat that figure as a baseline rather than current (Ofcom, 2021).
5. Business email compromise, invoice fraud and funds transfer fraud
This is where social engineering costs UK businesses the most money, and it is now the most frequent claim on most cyber insurers’ books. Our cyber insurance statistics page covers the claims side in full; the figures here are the ones about the attack itself.
UK figures
- Invoice and mandate scams, where a supplier’s bank details are changed by a criminal who has intercepted or compromised an email account, cost £41.3 million across 2,305 cases in 2025, the lowest totals on record; 68% of the losses (£28 million) were on business accounts, and 48% of losses were returned to victims (UK Finance Annual Fraud Report 2026).
- CEO fraud cost £5.6 million across 197 cases in 2025, down 53% and 29%, but it has the highest average case value of any APP scam type at just over £28,000, and only 20% of losses were recovered (UK Finance 2026).
- Taken together, the four “malicious redirection” scam types (invoice and mandate, CEO, police or bank impersonation, other impersonation) cost UK victims £139.3 million in 2025, all four at their lowest since records began in 2020, while total APP fraud rose 19% to £576.4 million on the back of investment and purchase scams (UK Finance 2026, our arithmetic from the published table).
- Email was recorded as the enabler in only 1% of APP fraud cases but 7% of losses, because the cases that start by email are the business ones (UK Finance 2026).
- Data from nine UK financial institutions covering over 100 million accounts showed a 62% rise in scam attempts in 2025, attributed to more social engineering, with phishing attempts up 140% (BioCatch, cited in UK Finance Annual Fraud Report 2026).
- BEC fell from 26% of Pinsent Masons’ UK caseload in 2024 to 17% in 2025; where it happened, 44% involved mailbox synchronisation and 33% led to invoice fraud (Pinsent Masons Cyber Annual Report 2026).
Insurer and global claims data
- Business email compromise and funds transfer fraud together were 58% of all Coalition claims in 2025; FTF alone was 27% of claims, BEC frequency rose 15%, the average BEC loss was £20,320 and the average FTF loss £106,136 (Coalition 2026 Cyber Claims Report, March 2026, over 100,000 policyholders in the UK, US, Canada, Australia and Germany).
- 52% of FTF claims originated as a BEC, and 71% of all FTF claims were a direct result of social engineering (Coalition 2026).
- Theft of funds was 25% of the cyber claims CFC resolved in 2025, the most common event type, and on 2026 notifications so far it is “approaching half of all cyber claims” (CFC, August 2026, global).
- Financial fraud was roughly 30% of At-Bay’s claims for the third year running; email was the initial entry vector in 82% of financial fraud claims and 52% of all claims, the average amount stolen was $285,000 (up 16%), and the largest single theft was $9.65 million (At-Bay InsurSec Report 2026, US-weighted).
- Policyholders who notified At-Bay within three days recovered at least some funds 70% of the time; after 30 days that fell to 27%. At-Bay recovered $56 million for clients in 2025 and Coalition £16.2 million at an average of £150,000 per recovery (At-Bay 2026; Coalition 2026).
- Losses tied to phishing, social engineering and transfer fraud rose from 17.7% of Resilience’s incurred losses in the first half of 2024 to 85.3% in the first half of 2026, while vendor-related losses fell from 81.5% to 2.3%; transfer fraud alone went from 2.9% to 9.2% of losses (Resilience Midyear Cyber Risk Report 2026, US-weighted).
- US victims reported $3.05 billion of BEC losses across 24,768 complaints in 2025, the second-largest loss category after investment fraud; tech support scams cost $2.13 billion and government impersonation $798 million (FBI IC3 2025 Internet Crime Report, US). 4,106 of IC3’s complaints came from the UK.
| Resilience portfolio, incurred losses by point of failure | H1 2024 | H2 2024 | H1 2025 | H2 2025 | H1 2026 |
|---|---|---|---|---|---|
| Social engineering | 17.7% | 41.3% | 46.9% | 75.2% | 85.3% |
| Vendor | 81.5% | 15.8% | 33.5% | 4.2% | 2.3% |
| Vulnerabilities | 0.8% | 25.2% | 16.3% | 9.9% | 7.0% |
| Governance | 0.0% | 15.5% | 1.7% | 6.9% | 5.4% |
Source: Resilience, 2026 Midyear Cyber Risk Report. Social engineering claim frequency over the same period moved from 11.9% to 21.7%, so the loss share rose much faster than the case count.
Suggested Read: Cyber Insurance Statistics
6. Deepfake and AI-enabled social engineering statistics
The honest position in 2026 is that AI has made social engineering more convincing, not more novel, and most of the hard numbers are still American. These are the ones with a method behind them.
- Deepfake impersonation was the most common AI-enabled attack type at 45%, ahead of AI-enabled malware (19%) and AI-generated phishing campaigns (17%); AI-driven attacks rose 56% in a year, and more than one in four organisations globally reported an AI-generated attack (IBM Cost of a Data Breach Report 2026, 602 organisations, breaches March 2025 to February 2026).
- 22% of UK organisations in the IBM sample reported AI-generated attacks (IBM 2026, UK).
- The FBI received 22,364 complaints that referenced AI in 2025, with adjusted losses above $893 million; businesses reported over $30 million lost to BEC scams involving AI, and victims lost over $5 million to “distress” scams using cloned voices of relatives (IC3 2025, US).
- By early 2025, AI-supported phishing campaigns reportedly represented more than 80% of observed social engineering activity worldwide, and AI is “notably used in vishing and online fraud involving impersonation” (ENISA, October 2025, citing vendor telemetry).
- Threat actors linked to China, Russia, Iran and North Korea are using large language models to support social engineering, and researchers have identified fully automated spear-phishing campaigns in the last 18 months (NCSC Annual Review 2025).
- Criminals are “crafting convincing impersonation scams and deploying deepfakes during account openings”, with synthetic identities and selfie injection used to pass identity checks; UK Finance publishes no count of deepfake cases (UK Finance Annual Fraud Report 2026).
- 45% of employees are now regular users of AI tools on corporate devices, up from 15% a year earlier, and 67% use personal accounts to do it, which widens what an attacker can learn about a target (DBIR 2026).
- A documented 2026 case: the CFO of a small financial services firm joined an audio-only Microsoft Teams meeting where AI-cloned voices of the CEO and a known transactional lawyer discussed an acquisition and instructed a wire transfer; the voice models had been trained on hours of the executives’ public audio and video (Resilience, 2026 Midyear Cyber Risk Report, insurer client, not UK).
The often-quoted Arup deepfake case is from early 2024 and we have left it out. If you need a UK deepfake fraud statistic for 2026, the IBM UK and IC3 figures above are the only ones we could trace to a published method.
7. Types of social engineering, in one line each
- Phishing: fraudulent email or websites to harvest credentials or deliver malware; 38% of UK businesses in 2025/26 (CSBS). See our phishing statistics page.
- Impersonation: someone posing as your organisation or staff in emails or online; 12% of UK businesses (CSBS 2025/26).
- Vishing: the same by phone, including police, bank and IT helpdesk impersonation; 11% of intrusions in 2025 (M-Trends 2026).
- Pretexting: a concocted scenario built over a call, chat or email thread to get an action out of the target; 6% of breaches by initial vector (DBIR 2026).
- Smishing: scam SMS, RCS or iMessage; received by 50% of UK mobile users in a quarter (Ofcom 2025).
- Business email compromise and funds transfer fraud: a compromised or spoofed mailbox used to redirect payments; 58% of Coalition claims (2026).
- MFA fatigue (push bombing): repeated MFA prompts until one is approved; a listed Scattered Spider technique (CISA/NCSC advisory, 2025).
- Helpdesk reset fraud: calling the service desk as an employee to reset a password or MFA token; the route the NCSC told retailers to close in May 2025.
- Deepfake and voice cloning: synthetic audio or video of an executive or relative; 45% of AI-enabled attacks (IBM 2026).
- Courier fraud: a “police officer” or “bank” sends a courier to collect cash or cards; 1,891 UK reports in 2025 (City of London Police).
- Baiting, ClickFix and SEO abuse: fake downloads, fake CAPTCHA pages and poisoned search results that get the user to run the malware themselves (DBIR 2026).
- Physical tailgating, shoulder surfing and dumpster diving: still practised, but there is no reliable published UK data on frequency, so we do not quote a figure.
8. Recent UK examples where the entry point was a person (2025 to 2026)
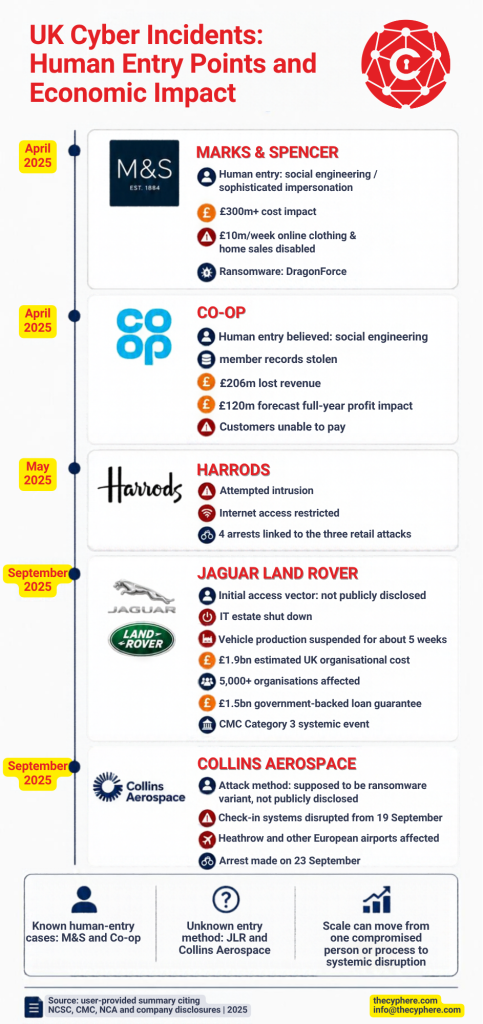
Marks & Spencer, April 2025. Chairman Archie Norman told the Business and Trade Committee on 8 July 2025 that initial entry took place on 17 April through “social engineering”, which he described as “sophisticated impersonation”, with a third party forming part of the point of entry. M&S estimated the gross profit impact at around £300 million before insurance recoveries, with online clothing and home sales disabled at a cost of roughly £10 million a week. The NCSC Annual Review 2025 puts the cost to M&S and its insurers at over £300 million and classes the attack as ransomware (DragonForce).
Co-op, April 2025. The NCSC confirms the data of all 6.5 million Co-op members was stolen in a DragonForce attack that also left customers unable to pay. Co-op’s interim results on 25 September 2025 put lost revenue at £206 million and the half-year operating profit hit at £80 million, with a full-year profit impact forecast of £120 million. The Cyber Monitoring Centre’s assessment of the two retail incidents says the initial access vector “is believed to be social engineering”, with reports of compromised credentials and “possible abuse of IT helpdesk processes”; it rated the pair a Category 2 systemic event costing £270 million to £440 million in total.
Harrods, May 2025. Harrods restricted internet access after an attempted intrusion in the same week. The NCA arrested two 19-year-old men, a 17-year-old boy and a 20-year-old woman in London and the West Midlands on 10 July 2025 on suspicion of Computer Misuse Act offences, blackmail, money laundering and participating in an organised crime group, in connection with all three retail attacks.
Jaguar Land Rover, September 2025. JLR shut down its IT estate in late August 2025 and suspended vehicle production at Solihull, Halewood and Wolverhampton for about five weeks, with a phased restart from 8 October. The government backed a £1.5 billion loan guarantee. The Cyber Monitoring Centre rated it a Category 3 systemic event and estimated the cost to UK organisations at £1.9 billion (range £1.6 billion to £2.1 billion), affecting over 5,000 organisations, calling it possibly the most economically damaging cyber event the UK has seen. JLR has not published the initial access vector, and the CMC notes that few technical details are public, so we do not attribute this one to social engineering. It sits here because the same criminal community claimed it and because it shows what a single entry point can now cost.
Collins Aerospace, September 2025. Check-in systems at Heathrow and other European airports were disrupted from 19 September. The NCA arrested a man in his forties in West Sussex on 23 September. The attack method has not been published.
We could not verify a 2026 UK incident with a confirmed social engineering entry point at a primary source by the time of writing; the NCSC reported in June 2026 that it managed more than 200 incidents affecting critical national infrastructure in the year to May 2026, but named none. We will add cases here as they are confirmed.
Suggested Read: Small Business Cyber Security Statistics
9. Staff training and testing: what UK organisations actually do
Every report above ends with a recommendation to train staff. The UK data on whether organisations do is less encouraging.
- 19% of UK businesses and 17% of charities ran any cyber security training or awareness activity in the last 12 months; the business figure was also 19% in 2024/25 and the charity figure fell from 21% (CSBS 2025/26).
- Training rises with size: 54% of medium businesses, 84% of large businesses (up from 76%, not a statistically significant change) and 49% of high-income charities (CSBS 2025/26).
- 22% of businesses and 13% of charities tested staff with mock phishing exercises; 13% of businesses had a penetration test (CSBS 2025/26).
- Among organisations that had a breach, “people or training changes” was the most common response, taken by 31% of businesses and 37% of charities (CSBS 2025/26).
- Only 7% of businesses and 8% of charities identified staff training and communications as a cyber security weakness, which suggests the gap is one of awareness as much as budget (CSBS 2025/26).
- The median click rate in 8,395 email phishing simulation campaigns was 1.4%, and the DBIR’s authors note that nearly all simulation data is email-based; they “struggled to find companies doing simulations of voice- and text message-based campaigns” (DBIR 2026).
Have a think about what those last two figures mean together. The attack vectors growing fastest are voice and helpdesk pretexting, and almost nobody is testing against them.
Frequently asked questions
What percentage of cyber attacks involve social engineering?
It depends on the definition. The human element (error, misuse, stolen credentials or social engineering) was present in 62% of breaches worldwide in the 2026 Verizon DBIR; the narrower Social Engineering attack pattern was 16% of breaches. In Europe, ENISA puts phishing including vishing at about 60% of observed initial intrusions. Figures of 90% to 98% that circulate online have no traceable source.
How many UK businesses are affected by social engineering?
12% of UK businesses and 7% of charities identified impersonation of their organisation or staff in 2025/26, and 38% of businesses identified phishing. Among large businesses the impersonation figure is 47% (Cyber Security Breaches Survey 2025/26).
What is the most common type of social engineering attack in 2026?
By volume, phishing by email, then text and voice. By money lost to businesses, business email compromise and funds transfer fraud: 58% of Coalition’s 2025 claims and the most common claim type at CFC and At-Bay. In the UK, invoice and mandate scams cost £41.3 million and police or bank impersonation £55.5 million in 2025 (UK Finance).
How much does social engineering cost UK businesses?
There is no single UK total. UK Finance recorded £139.3 million lost to the four impersonation and redirection scam types in 2025, most of it reimbursed to consumers but not to businesses (48% of invoice scam losses and 20% of CEO fraud losses were returned). The M&S and Co-op attacks alone are estimated at £270 million to £440 million (Cyber Monitoring Centre). Globally, the average BEC claim was £20,320 and the average funds transfer fraud claim £106,136 (Coalition 2026).
Is vishing increasing?
Yes, in organisations. Voice phishing was the second most common intrusion vector in 2025 at 11%, ahead of email phishing at 6% (Mandiant M-Trends 2026), and pretexting became a more common route into ransomware attacks (DBIR 2026). For UK consumers the picture is better: police and bank impersonation losses fell 18% in 2025 and suspicious text receipt has fallen from 75% of mobile users in 2021 to 50% in 2025 (UK Finance; Ofcom).
Are deepfakes being used in fraud in the UK?
UK Finance says criminals are deploying deepfakes during account opening but does not publish a count. 22% of UK organisations in IBM’s 2026 sample reported AI-generated attacks, and deepfake impersonation was the most common AI-enabled attack type at 45% globally. US victims reported over $893 million of losses in AI-related complaints to the FBI in 2025.
About this data
This page draws on reports published between May 2025 and September 2026. UK prevalence and training figures are from the DSIT Cyber Security Breaches Survey 2025/26 (fieldwork August to December 2025, published 30 April 2026). UK fraud losses are from the UK Finance Annual Fraud Report 2026 (2025 data, published June 2026), City of London Police (courier fraud, June 2026) and the ONS Crime Survey for England and Wales (year to March 2026). Consumer scam call and text figures are from Ofcom’s 2025 research as cited in its October 2025 consultation on mobile messaging scams. Incident figures are from the NCSC Annual Review 2025 (September 2024 to August 2025). Global breach data is from the Verizon 2026 DBIR, ENISA’s 2025 threat report, Mandiant M-Trends 2026, Microsoft’s Digital Defense Report 2025, IBM’s Cost of a Data Breach Report 2026 and the FBI IC3 2025 report; claims data is from Coalition, CFC, At-Bay, Resilience and Pinsent Masons, and we have labelled each by geography. ICO figures are our own count of unique incident references in the ICO’s data security incident trends dataset (Q1 2019 to Q4 2025). The £139.3 million UK malicious redirection total is our own sum of the four scam types in UK Finance’s published table.
All figures from 2020 to 2023 that appeared in previous versions of this page, including the unsourced “98% of attacks” line and the US vishing and smishing volumes, have been removed. We refresh this page after each Cyber Security Breaches Survey (April), UK Finance Annual Fraud Report (June) and Verizon DBIR (May).
If you cite a figure from this page, please link to the original source as well as to us; the references are below.
References
- DSIT, Cyber Security Breaches Survey 2025/26 (30 April 2026)
- UK Finance, Annual Fraud Report 2026 (June 2026)
- UK Finance, press release (15 June 2026)
- City of London Police, courier fraud exceeds £21 million in 2025 (15 June 2026)
- Ofcom, Experiences of suspicious calls, texts and app messages 2025, as cited in Combatting mobile messaging scams consultation (29 October 2025)
- Ofcom, Tackling scam calls from abroad consultation (21 July 2025)
- Ofcom, 45 million people targeted by scam calls and texts (October 2021)
- NCSC Annual Review 2025 (14 October 2025)
- NCSC, Incidents impacting retailers (4 May 2025)
- NCSC, hostile states linked to three-quarters of attacks on critical systems (17 June 2026)
- ONS, Crime in England and Wales: year ending March 2026 (23 July 2026)
- ICO, Data security incident trends dataset
- Cyber Monitoring Centre, statement on ransomware incidents in the retail sector (20 June 2025)
- Cyber Monitoring Centre, statement on the Jaguar Land Rover cyber incident (22 October 2025)
- House of Commons Business and Trade Sub-Committee, oral evidence from M&S (8 July 2025)
- National Crime Agency, four arrested for attacks on M&S, Co-op and Harrods (10 July 2025)
- National Crime Agency, UK arrest following aerospace cyber incident (24 September 2025)
- Retail Gazette, Co-op interim results (25 September 2025)
- CISA, FBI and partners, Scattered Spider advisory AA23-320A (updated 29 July 2025)
- Verizon, 2026 Data Breach Investigations Report (19 May 2026)
- Verizon, 2026 DBIR press release (19 May 2026)
- ENISA Threat Landscape 2025 (1 October 2025, v1.3 September 2026)
- Google Cloud / Mandiant, M-Trends 2026 (23 March 2026)
- Microsoft, Digital Defense Report 2025 summary (16 October 2025)
- IBM, Cost of a Data Breach Report 2026, UK findings (28 July 2026)
- FBI IC3, 2025 Internet Crime Report
- Proofpoint, 2026 AI-Era Ransomware Report press release (22 July 2026)
- Pinsent Masons, Cyber Annual Report 2026
- Coalition, 2026 Cyber Claims Report (UK)
- Coalition, UK announcement of the 2026 Cyber Claims Report (6 March 2026)
- CFC, Theft of funds: the most common cyber claim today (27 August 2026)
- At-Bay, 2026 InsurSec Report (April 2026)
- Resilience, 2026 Midyear Cyber Risk Report (August 2026)